ShinyHunters / UNC6240 - Oracle PeopleSoft WAF Bypass Campaign
ShinyHunters UNC6240 Oracle PeopleSoft CVE-2026-35273 WAF Bypass
Overview
ShinyHunters resumed large-scale exploitation of Oracle PeopleSoft CVE-2026-35273 after many organizations attempted mitigation through WAF blocking rules rather than patching vulnerable systems.
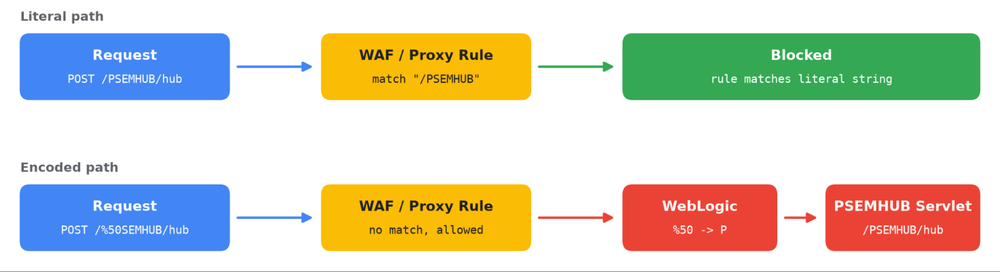
Attackers modified requests by URL-encoding part of the vulnerable PSEMHUB path, allowing some WAF implementations to miss malicious traffic while backend systems decoded and routed requests to the vulnerable component. Public reporting indicates web shells were deployed on dozens of systems globally.
Technical Details
Vulnerable Component
- Product area: Oracle PeopleSoft PeopleTools Environment Management Hub (PSEMHUB/EMHub).
- Exploitability: remote, unauthenticated.
- Primary risk: remote code execution.
WAF-Bypass Mechanism
- Original target path:
/PSEMHUB/ - Bypass variant:
/%50SEMHUB/(%50URL-decodes toP). - Some defensive controls reportedly inspected literal URL strings before normalization/decoding.
- Backend decoding then restored the effective path to
PSEMHUB, enabling exploit traffic to reach target servlet logic.
Post-Exploitation Behavior
- Java deserialization abuse used for command execution.
- JSP web shells reported, including
x.jspandu.jsp. - Follow-on access/tunneling and potential data theft opportunities observed in campaign reporting.
Technical Specifications
| Attribute | Details |
|---|---|
| Campaign Actor Labeling | ShinyHunters / UNC6240 (public reporting context) |
| Primary CVE | CVE-2026-35273 |
| Exposed Surface | PeopleTools Environment Management Hub (PSEMHUB) |
| Attack Type | Unauthenticated RCE via deserialization path |
| Evasion Technique | URL-encoding WAF bypass (/%50SEMHUB/) |
| Persistence Indicator | JSP web-shell deployment on compromised servers |
Affected Products
- Oracle PeopleSoft deployments exposing vulnerable PeopleTools EMHub/PSEMHUB functionality.
- WebLogic-backed PeopleSoft environments where patching was delayed and WAF-only mitigations were applied.
Attack Scenario
- Attacker identifies internet-exposed or otherwise reachable unpatched PeopleSoft target.
- Malicious POST requests are sent to PSEMHUB servlet paths.
- Encoded path variant (
/%50SEMHUB/) bypasses literal WAF rules in some environments. - Java deserialization exploitation yields remote code execution.
- JSP web shells are deployed for persistence/command execution.
- Adversary establishes additional access paths, potentially tunnels traffic, and may exfiltrate data.
- Compromised PeopleSoft infrastructure is reused for follow-on activity.
Impact Assessment
- Full server compromise potential via unauthenticated RCE
- Persistent web-shell footholds on enterprise systems
- Credential theft and lateral movement opportunities
- Potential exposure of HR, payroll, student, and other highly sensitive enterprise data in PeopleSoft ecosystems
- Risk of significant downstream operational and compliance impact from long-lived compromise
- Critical due to active exploitation, bypass of weak compensating controls, and widespread enterprise data sensitivity in PeopleSoft environments
Mitigation Strategies
Patch and Exposure Control
- Apply Oracle patch for CVE-2026-35273 immediately.
- Do not rely solely on WAF URL-blocking rules.
- Disable EMHub where feasible, or remove PSEMHUB application in applicable single-server deployments.
Detection and Threat Hunting
- Review WebLogic logs for
/PSEMHUB/and encoded variants such as/%50SEMHUB/. - Inspect
PSEMHUB.warfor unauthorized JSP artifacts. - Validate all WebLogic nodes, including load-balanced nodes, for consistent compromise checks.
Post-Compromise Hardening
- Rotate credentials accessible to PeopleSoft service accounts.
- Monitor outbound connections from PeopleSoft servers and investigate suspicious remote-management tooling.
- Hunt for persistence, tunneling utilities, and unexpected administrative agents.
Resources and References
Public Reporting
Last Updated: September 29, 2026