Last Week's Security Incidents
-
US Government Accuses Chinese AI Firms of Distilling Frontier Models
AI Security Model Distillation IP Extraction Risk Service Abuse Strategic Competition
U.S. agencies allege industrial-scale extraction of proprietary frontier-model capabilities through distributed high-volume model interactions, while China publicly disputes the claims.
-
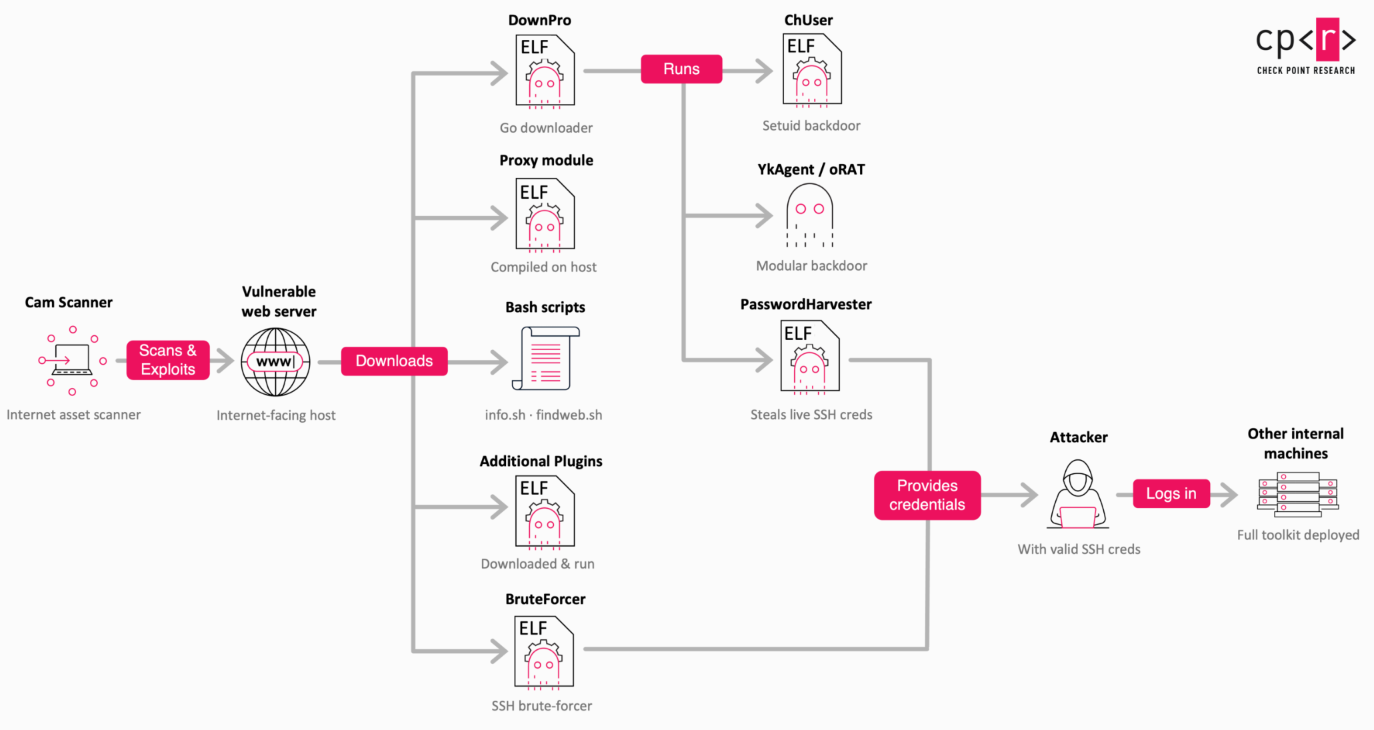
Brazilian Government Traffic Hijacking Campaign
Traffic Hijacking Malicious Apache Modules SEO Poisoning Government Domains Gambling Goblin
A reported Chinese-speaking group hijacked traffic on compromised Brazilian government and education domains using malicious Apache modules that proxied visitors to phishing and betting content.
-
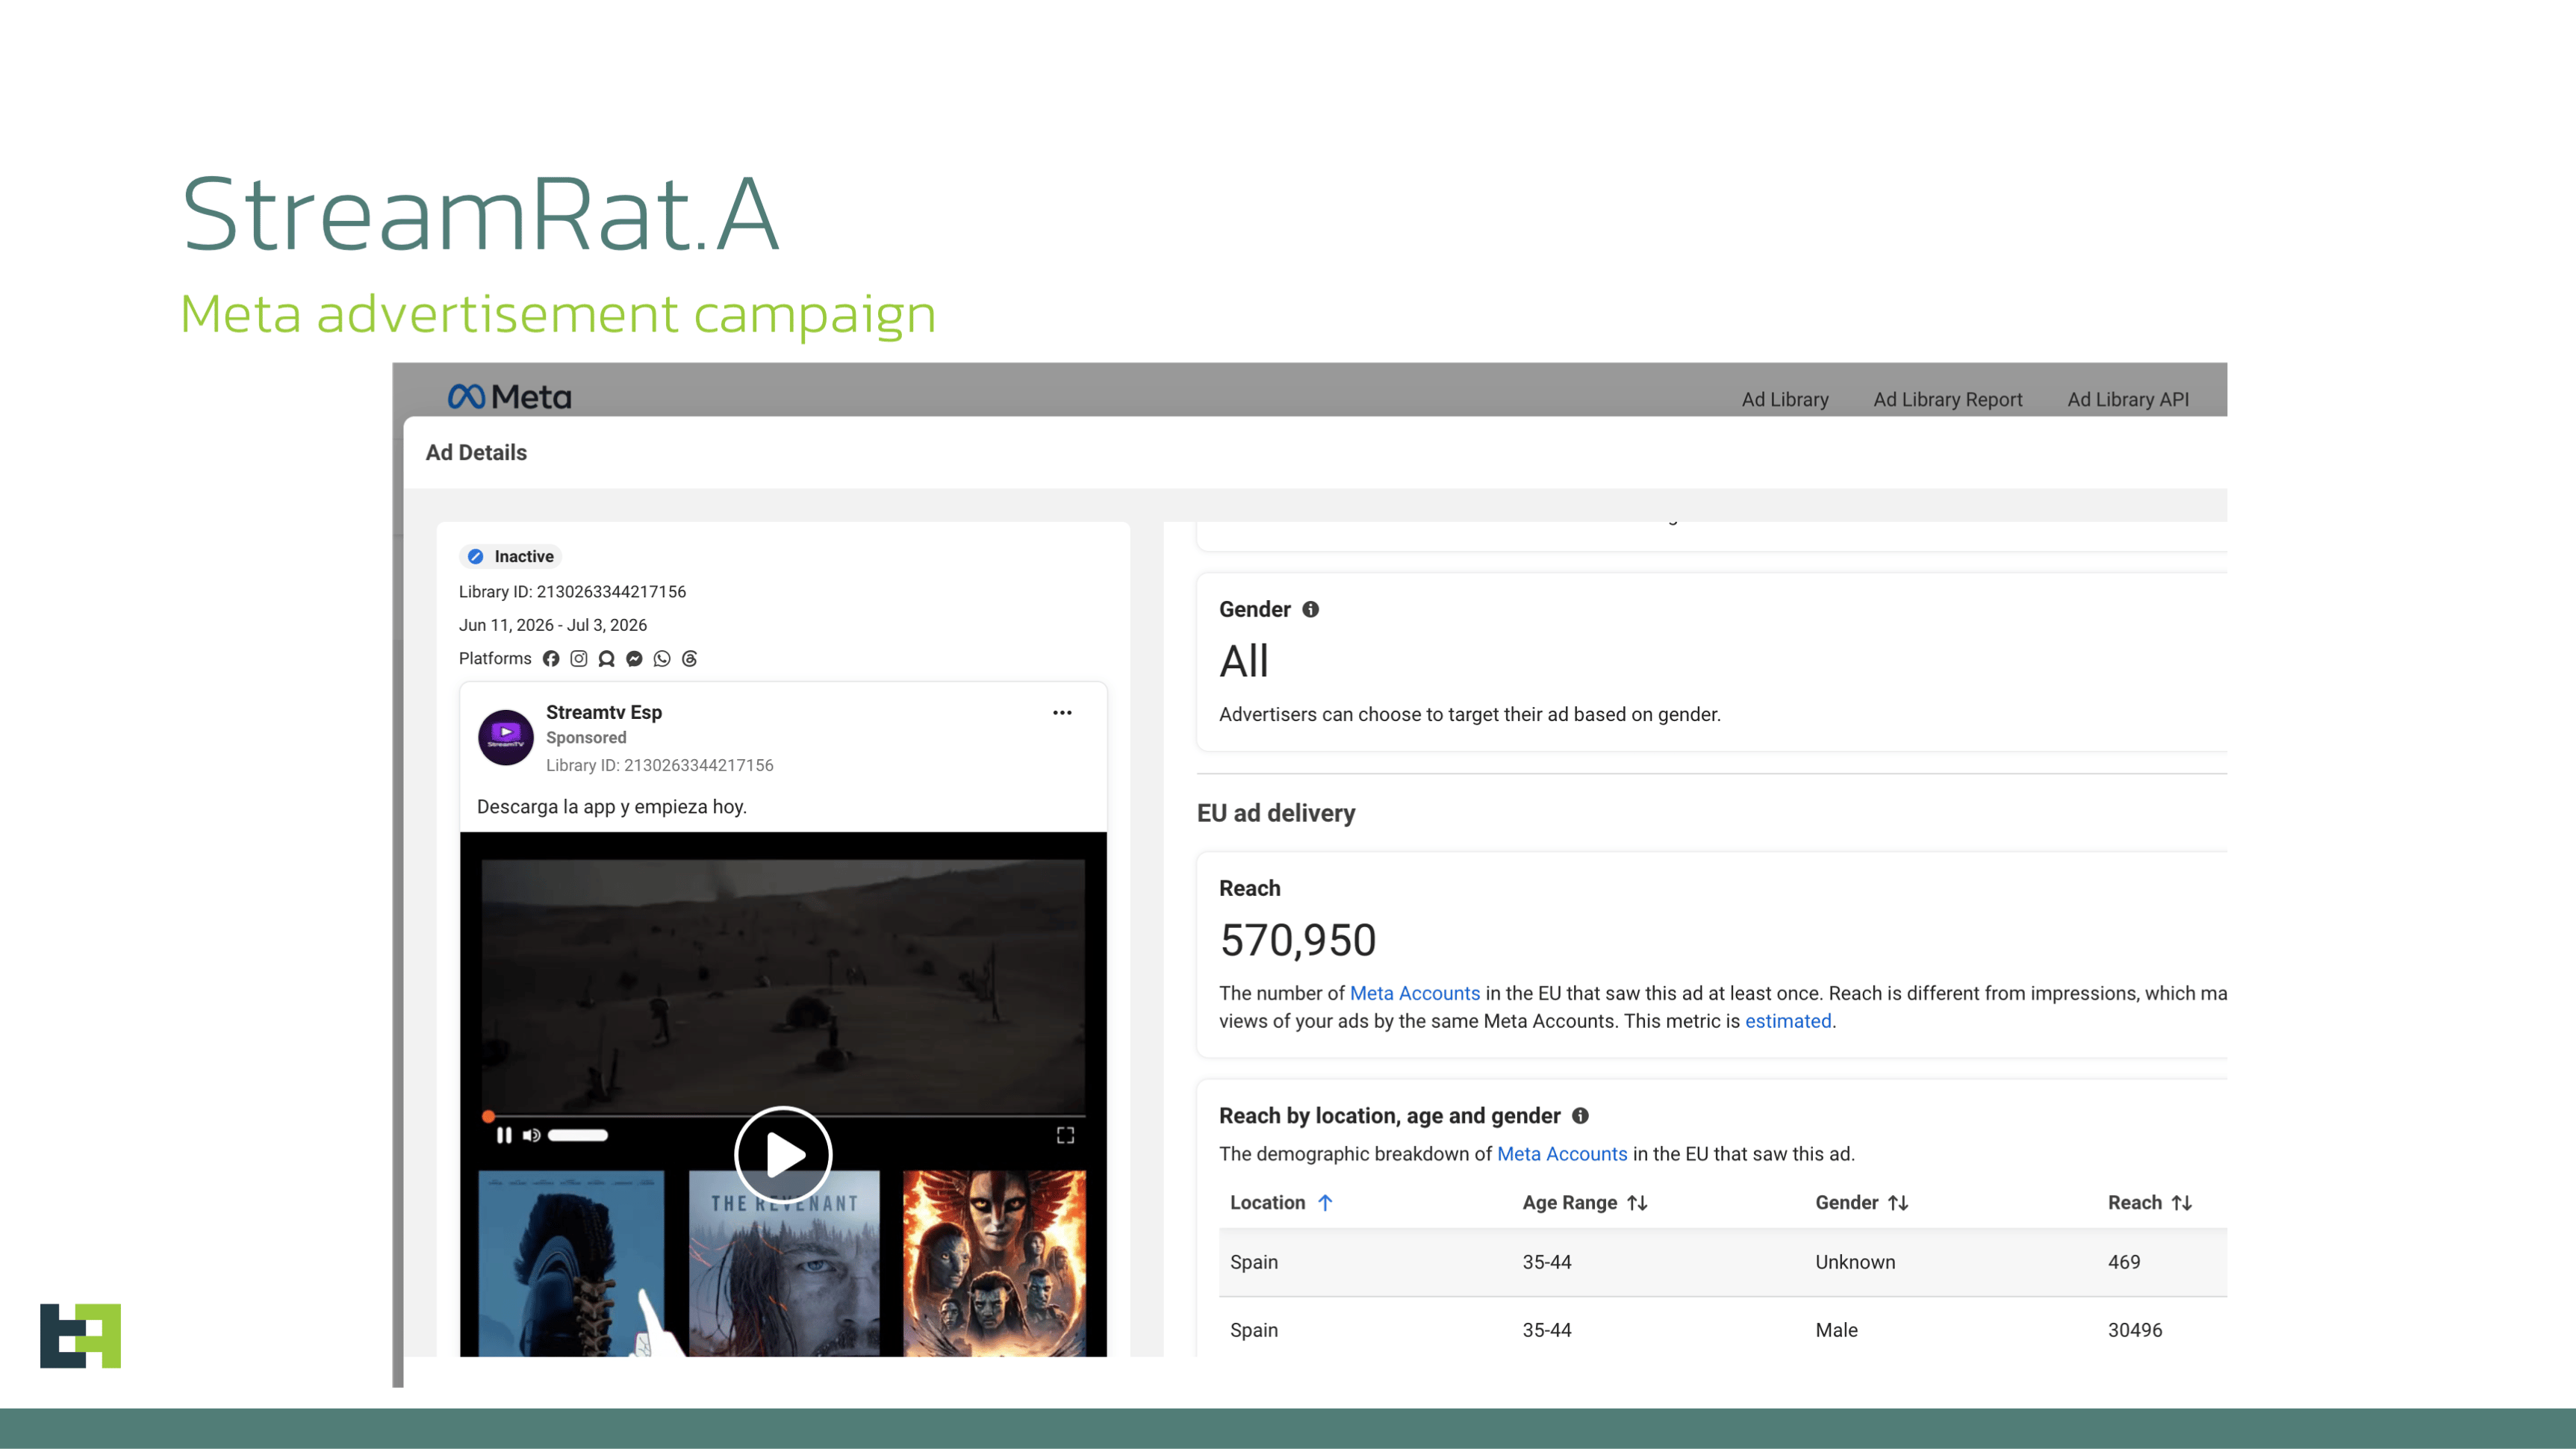
Meta Ads Push StreamRat Android Trojan That Can Gain Near-Complete Device Control
Android Trojan Malvertising StreamRat Accessibility Abuse Remote Device Control
StreamRat is being spread through malicious ad-to-sideload chains that abuse Accessibility permissions for credential theft, overlays, and near-complete remote control of infected Android devices.
-
MikroTrick: Actively Exploited MikroTik RouterOS SSH Attack Chain
Active Exploitation MikroTik RouterOS SSH Exposure CVE-2026-67276 CVE-2026-86060
CERT Polska reported active exploitation of a two-CVE RouterOS SSH chain that can grant full administrative control of internet-exposed MikroTik devices, requiring urgent patching and compromise review.
-
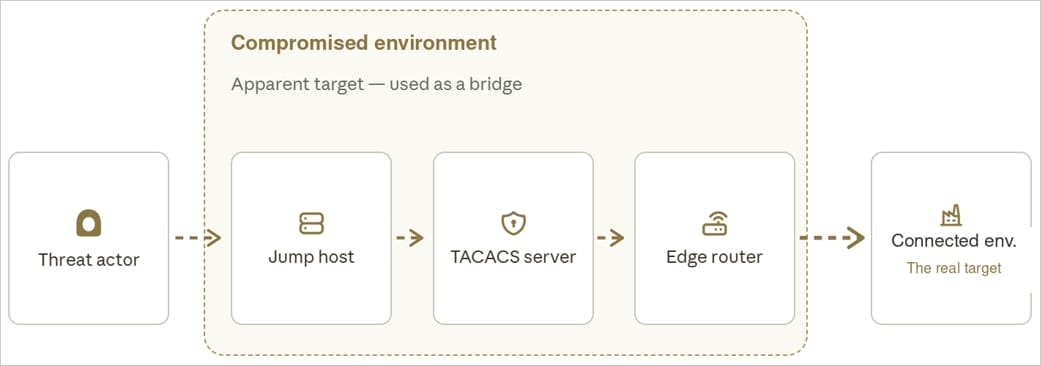
Fire Ant - China-linked Cyber Espionage Campaign Targeting Trusted Infrastructure
Cyber Espionage Trusted Infrastructure Cisco IOS XR TACACS Credential Theft Linux Backdoors Covert Tunneling
Fire Ant reportedly compromised trusted router, TACACS, and Linux management layers to intercept credentials, suppress telemetry, and pivot toward higher-value target networks.
-
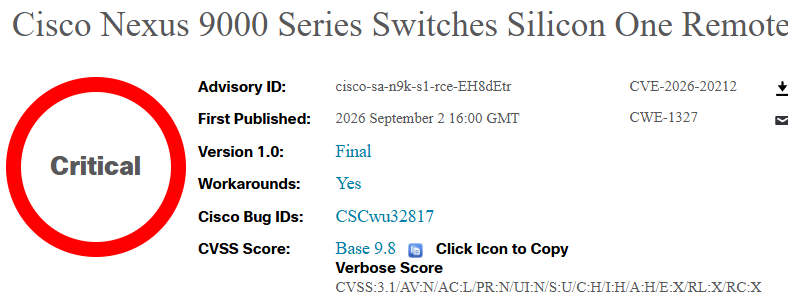
CVE-2026-20212 - Cisco Nexus 9000 Series Switches Silicon One Remote Code Execution Vulnerability
Critical RCE Cisco Nexus 9000 Silicon One Unauthenticated Attack Root Privileges NX-OS
Cisco fixed a critical Silicon One integration flaw in certain Nexus 9000 switches that could allow remote unauthenticated root-level code execution or trigger S1HAL crashes and device reloads.
-
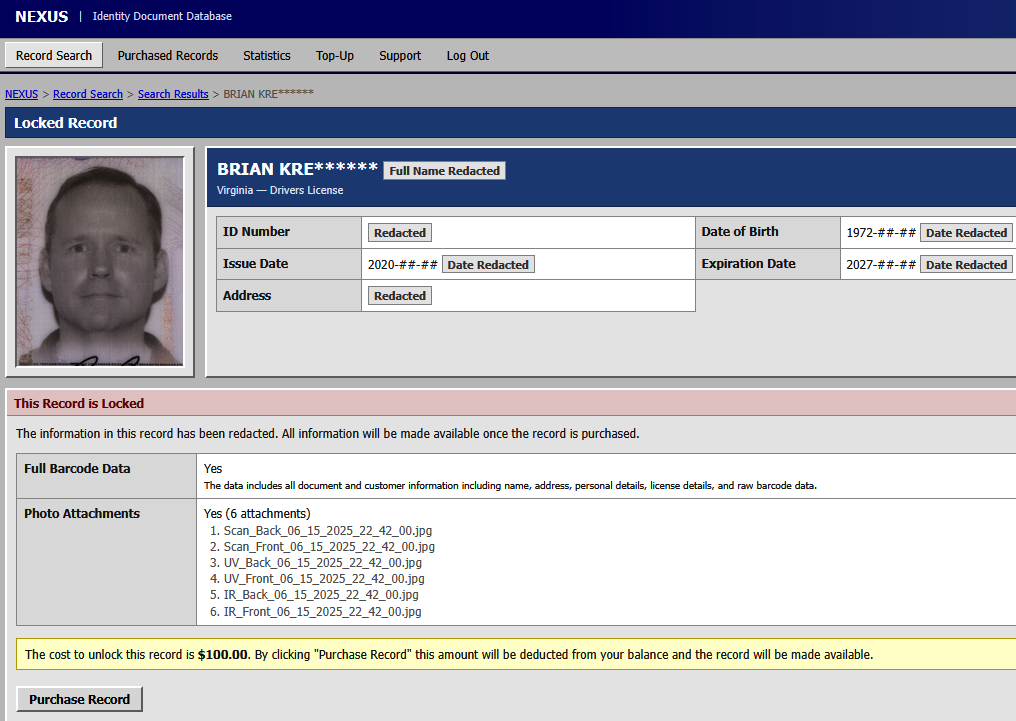
Dark Web Service Nexus Sells 153M+ Driver's Licenses
Dark Web Marketplace Identity Data Exposure Driver License Records Potential PII Breach Fraud Risk Investigation Ongoing
Nexus advertised searchable access to massive identity-document datasets, including 153M+ claimed driver's licenses, creating significant long-term fraud and impersonation risk while source attribution remains under investigation.
-
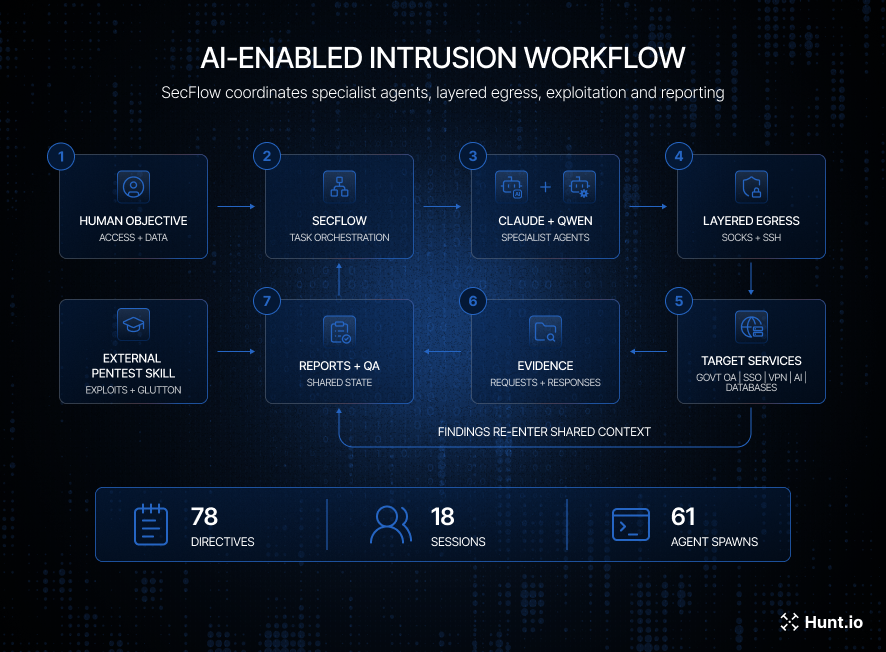
Chinese Hackers Use AI Agents in Multi-Country Cyber Campaign
AI-Enabled Threat Activity Cyber Espionage SecFlow GLUTTON Webshell Credential Theft Data Exfiltration
Hunt.io reported a Chinese-speaking threat actor using SecFlow to orchestrate AI-model-driven reconnaissance, exploitation, credential theft, and data exfiltration across multi-country targeting.