Mercedes-Benz USA Breach Claim by Threat Actor 'zestix'
Data Breach Claim
Legal & Customer Data
Dark Web Sale
Overview
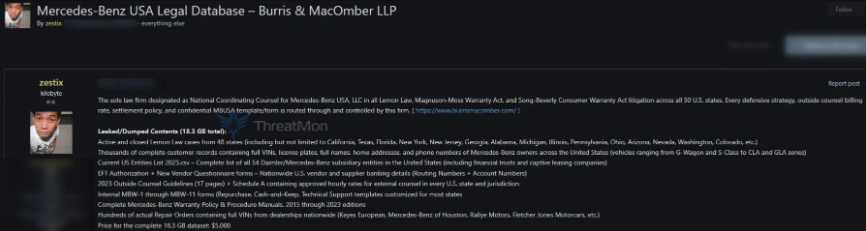
According to the claim by threat actor 'zestix', about 18.3 GB of data was exfiltrated from Mercedes-Benz USA (MBUSA), including internal legal documents (active and closed litigation files across 48 U.S. states), customer data / PII, vendor forms, defensive strategies, billing rates, settlement policies, and documents related to warranty claims under laws like the Magnuson-Moss Warranty Act and the Song-Beverly Consumer Warranty Act. The actor is reportedly selling the archive on a dark-web forum for USD 5,000.
Technical Specifications
| Attribute | Details |
|---|---|
| Threat Actor | 'zestix' |
| Claimed Data Size | 18.3 GB |
| Target Organization | Mercedes-Benz USA (MBUSA) |
| Data Types | Legal documents, customer PII, vendor forms, billing rates, settlement policies |
| Sale Price | USD 5,000 (on dark-web forum) |
| Verification Status | Unconfirmed — MBUSA has not publicly verified authenticity |
Technical Details
Very limited public information available: - The report does not provide clear details on how the alleged breach happened - Method of intrusion is unknown (e.g., vulnerability exploited, third-party vendor compromise, misconfiguration, or insider) - The "attack vector" is not described in available sources
Claimed Data Contents
-
Internal Legal Documents:
- Active and closed litigation files across 48 U.S. states
- Defensive strategies
- Settlement policies
-
Customer Data / PII:
- Personal identifiable information
- Warranty claim data
-
Vendor Information:
- Vendor forms
- Billing rates
- Financial data
-
Regulatory Documents:
- Documents related to Magnuson-Moss Warranty Act
- Song-Beverly Consumer Warranty Act compliance
Attack Scenario
-
Data Exfiltration (Claimed): The threat actor claims to have exfiltrated legal and customer data from MBUSA (or its legal / vendor systems).
-
Dark Web Posting: The data was posted for sale on a dark-web forum for USD 5,000.
-
Data Exposure: The breach supposedly compromises:
- MBUSA's legal infrastructure (defense strategies, litigation history, vendor data)
- Customer PII
Impact Assessment
- Exposure of sensitive legal strategy documents
- Could undermine ongoing or future litigation / warranty-claim defenses
- Competitive disadvantage in legal proceedings
- Leak of customer PII: personal data, contact info and other sensitive identifiers
- Risk of identity theft, fraud, targeted phishing
- Increased risk for customers involved in warranty or legal claims to be targeted by scams/phishing referencing their case files
- Exposure of vendor-related data (billing rates, financial data)
- Risk of financial fraud or vendor compromise
- Reputational damage to Mercedes-Benz / MBUSA if confirmed
- Loss of customer trust
- Potential regulatory scrutiny
Mitigations
⚠️ Important Note
Because the claim is unconfirmed and neither MBUSA nor the alleged vendor has publicly verified authenticity of the leak, vigilance is recommended.
👥 For Affected Customers
- Monitor credit reports and personal data regularly
- Be alert to phishing or scam attempts referencing customer data or case files
- Watch for suspicious communications claiming to be from Mercedes-Benz or related to warranty claims
🏢 For Mercedes-Benz / MBUSA
- Investigate and publicly confirm or deny the breach claim
- Audit vendor access controls, assess scope of data exposure
- Conduct legal/third-party vendor risk assessment
- Implement tighter data-handling controls for customer and internal legal data
- Provide transparency with affected individuals if breach confirmed
🔒 General Recommendations
- Review and strengthen access controls for sensitive legal and customer data
- Implement data loss prevention (DLP) solutions
- Conduct regular security audits of third-party vendors
- Enhance monitoring and logging for sensitive data access
Resources & References
Verification Status
This breach claim remains unconfirmed by Mercedes-Benz USA as of the time of this documentation. Monitor official Mercedes-Benz communications for updates.