Lantronix EDS5000 Critical Vulnerability Exploitation (CVE-2025-67038)
CVE-2025-67038
OS Command Injection
Lantronix EDS5000 / OT Edge Device
Overview
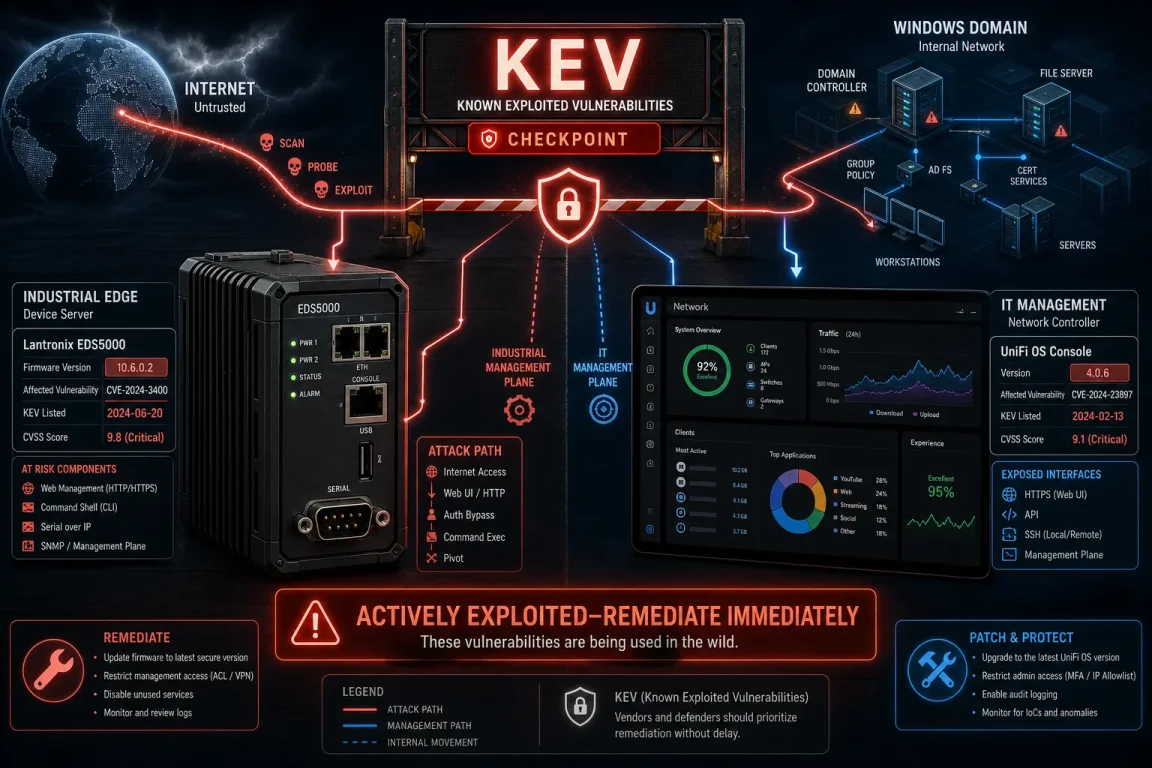
A critical vulnerability affecting Lantronix EDS5000 Series serial device servers, tracked as CVE-2025-67038, is reportedly being actively exploited in the wild. The flaw allows remote attackers to execute arbitrary operating system commands on affected devices, potentially leading to full device compromise and subsequent lateral movement into internal IT or OT networks. Public reporting also references CVE-2025-67037 as a related issue that may impact the same platform and increase overall risk exposure.[web:56][web:58]
Technical Specifications
| Attribute | Details |
|---|---|
| CVE ID | CVE-2025-67038 (primary); CVE-2025-67037 (related) |
| Vulnerability Type | OS command injection in management interface of serial device server |
| CVSS Score | Critical (vendor and CISA advisories classify as high/critical severity) |
| Attack Vector | Network (internet-exposed or reachable management interfaces) |
| Authentication | Often low or none, depending on configuration and exposure |
| Complexity | Low to Medium |
| User Interaction | Not Required |
| Affected Versions | Lantronix EDS5000 Series serial device servers with vulnerable firmware; devices exposed to the internet or improperly segmented are at highest risk |
Affected Products
- Lantronix EDS5000 Series serial device servers
- OT and industrial networks where EDS5000 devices provide serial-over-IP connectivity
- Enterprise environments that integrate EDS5000 devices into remote management or telemetry solutions
- Deployments with internet-exposed, weakly authenticated, or poorly segmented management interfaces
Attack Scenario
- An attacker scans the internet or reachable ranges for exposed Lantronix EDS5000 management interfaces.
- A vulnerable device is identified, often with limited authentication or misconfigured access controls.
- The attacker sends crafted malicious requests that exploit the OS command injection vulnerability (CVE-2025-67038, and potentially CVE-2025-67037).
- Successful exploitation yields remote command execution, typically with elevated or root privileges on the device.
- The attacker uses remote shell access to install persistence mechanisms, modify configurations, or pivot into attached OT/IT networks.
- The compromised device becomes an entry point for espionage, data theft, lateral movement, or ransomware deployment in critical infrastructure environments.
Impact Assessment
Integrity
- Attackers can run arbitrary system commands, modify configuration, and alter device behavior.
- Root-level access enables tampering with serial data flows and operational logic at the edge of OT networks.
- Compromised devices may be reconfigured to support backdoors or malicious monitoring.
Confidentiality
- Serial-to-IP traffic and any data handled by EDS5000 devices may be exposed or inspected.
- Attackers may harvest credentials, configuration files, and network information from compromised devices.
- Access to OT gateways increases the risk of sensitive process data or telemetry being exfiltrated.
Availability
- Malicious command execution can disrupt device operation and upstream/downstream communications.
- Critical infrastructure relying on EDS5000 connectivity may face outages or degraded performance.
- Ransomware or destructive actions launched from compromised devices can impact broader plant or enterprise availability.
Mitigation Strategies
Immediate Actions
- Apply vendor security patches and firmware updates for Lantronix EDS5000 devices as soon as they are available.
- Remove affected devices from direct internet exposure and place management interfaces behind secure access controls.
- Rotate administrative credentials on EDS5000 devices and related management systems if compromise is suspected.
Short-term Measures
- Restrict administrative access via VPNs, jump hosts, and strict ACLs; avoid exposing management ports on public IP space.
- Segment OT and IT environments, ensuring that EDS5000 devices reside in appropriately protected network zones.
- Implement least-privilege access policies for accounts managing Lantronix infrastructure and OT gateways.
Monitoring & Detection
- Monitor device and syslog output for suspicious command execution, unusual process activity, or configuration changes.
- Conduct threat hunting and IOC analysis focused on known exploit patterns for CVE-2025-67038/CVE-2025-67037.
- Review inbound connections, authentication logs, and remote management sessions for anomalies, especially on internet-facing devices.
Resources and References
Official Documentation
Last Updated: June 25, 2026