ABB Ability Edgenius Authentication Bypass – CVE-2025-10571
CVE-2025-10571
Authentication Bypass
Adjacent Network Access
Overview
CVE-2025-10571 is a critical authentication bypass vulnerability in ABB Ability Edgenius, an industrial edge computing and management platform. Due to improper access controls, an attacker on the adjacent network can directly interact with the Edgenius Management Portal and execute privileged operations without authentication.
This could allow attackers to install, modify, or uninstall software packages, reconfigure systems, or take control of edge nodes within an industrial environment.
Technical Specifications
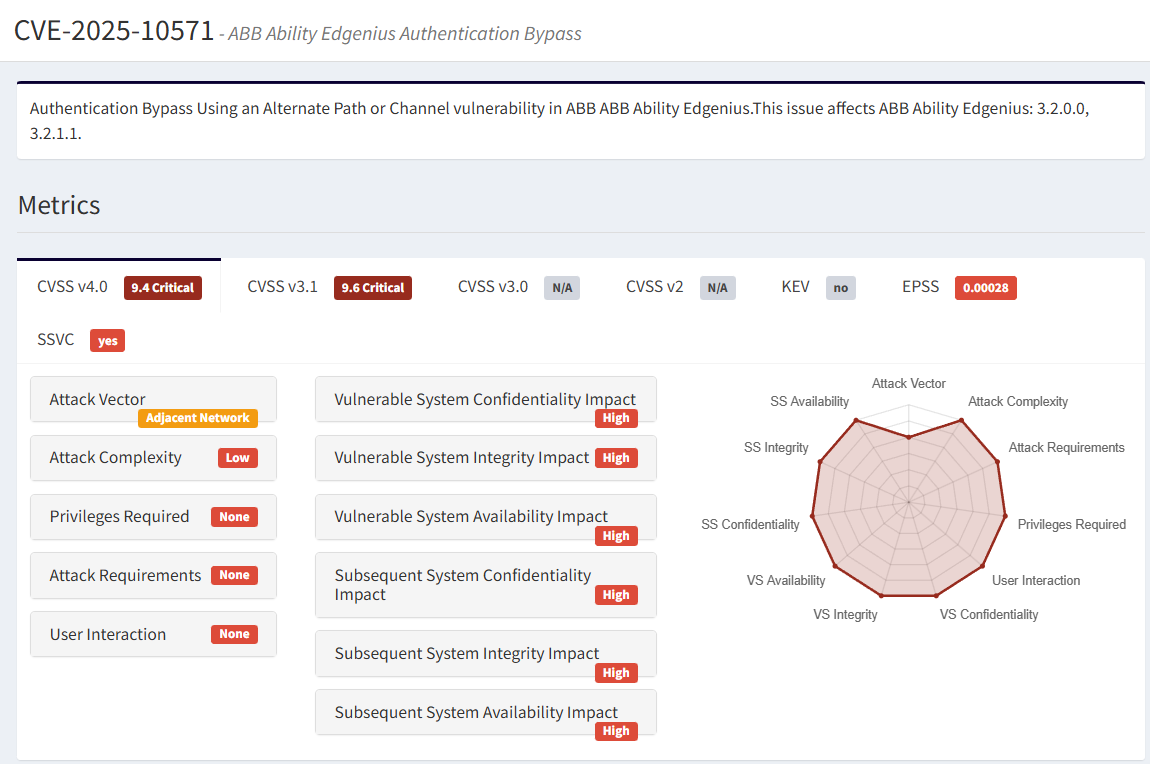
| Attribute | Details |
|---|---|
| CVE ID | CVE-2025-10571 |
| Vulnerability Type | Authentication Bypass / Alternate Path |
| Attack Vector | Adjacent Network (local segment, routed industrial network, VPN) |
| Authentication | None required |
| Complexity | Low |
| User Interaction | None required |
| Affected Component | ABB Ability Edgenius Management Portal |
Affected Versions
- 3.2.0.0
- 3.2.1.1
Root Cause
A backend API used by the Edgenius Management Portal does not properly enforce authentication checks, enabling unauthorized access from an attacker with network visibility into the node hosting Edgenius.
Vulnerability Class
CWE-288 – Authentication Bypass / Alternate Path
Scope: Changed – exploitation can affect external systems via control plane compromise.
Attack Scenario
- An attacker gains access to the same network segment or route as an Edgenius node (e.g., via lateral movement, exposed VLAN, misconfigured firewall, or VPN access).
- They send crafted requests to the Edgenius management API.
- Due to missing authentication validation, the system accepts the request as legitimate.
- The attacker can then:
- Install or remove applications on edge systems
- Modify configuration or operational parameters
- Deploy malicious code
- Disrupt industrial processes
Compromise of the edge manager can enable pivoting deeper into OT or industrial networks.
Impact Assessment
- Unauthenticated access to edge device configuration and operational data
- Attackers can change system settings
- Push unauthorized apps or inject malicious payloads
- Industrial functions may be disabled
- Applications removed or systems rendered inoperable
- Loss of visibility or control over production edge devices
- Compromise of industrial automation processes
- Potential for operational downtime, safety violations, or manipulation of production logic
- Gateway takeover allowing further attacks on PLCs, SCADA, or industrial controllers
Mitigations
🔄 Primary Mitigation (Recommended)
Upgrade to ABB Ability Edgenius version 3.2.2.0 or later, which contains the official fix.
🛡️ If Patching is Delayed
- Disable the Edgenius Management Portal if not required.
- Restrict network access to Edgenius nodes:
- Firewall rules
- VLAN segmentation
- Zero-trust zone enforcement
- Do not expose Edgenius management services to the Internet or uncontrolled networks.
📊 Implement
- IDS/IPS monitoring for suspicious requests
- System logging of management operations
- Strong access controls on administration paths
🔍 Assess Edge Nodes For
- Unexpected installed applications
- Unauthorized configuration changes
- Signs of lateral movement on the OT network
Resources & References
Official & Advisory Resources