Nihon Kohden CNS-6201 Central Monitor Vulnerability
Overview
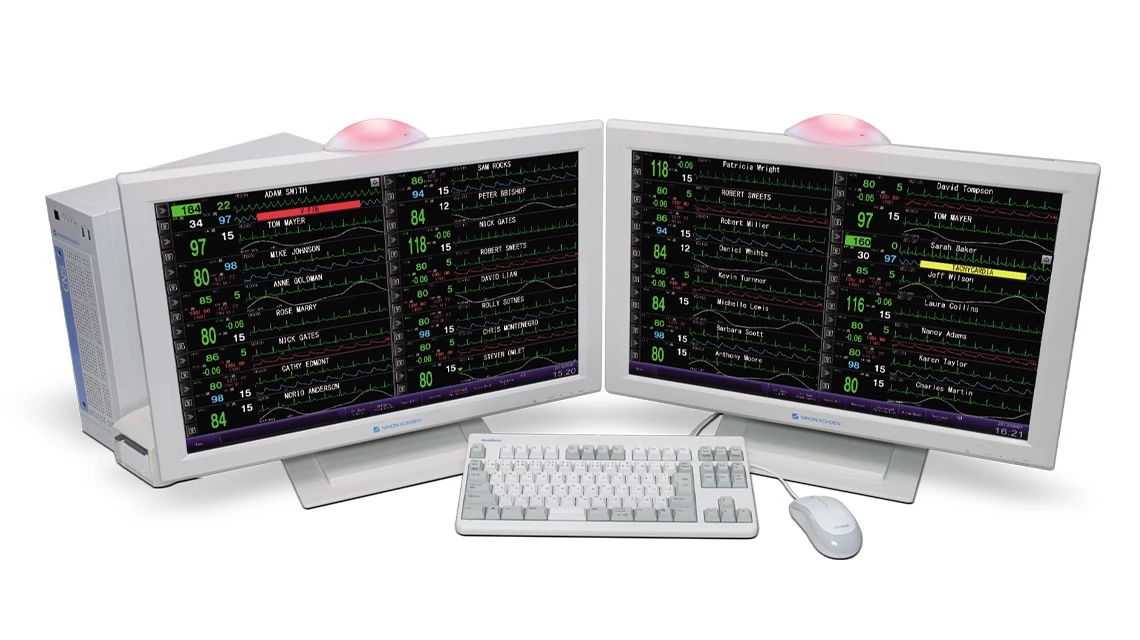
A critical vulnerability in the Nihon Kohden CNS-6201 central monitoring system allows remote attackers to crash the system through malformed UDP packets, resulting in loss of patient monitoring capabilities.
Technical Specifications
| Attribute | Details |
|---|---|
| CVE ID | CVE-2025-59668 |
| Vulnerability Type | NULL pointer dereference (CWE-476) |
| Attack Vector | Network-based (UDP) |
| Authentication | None required |
| CVSS Score | High (Availability Impact) |
Affected Versions
- CNS-6201 software versions: 01-03, 01-04, 01-05, 01-06, 02-10, 02-11, and 02-40
Attack Scenario
- Attacker gains network access to medical device network
- Sends malformed UDP packet to CNS-6201's open UDP port
- Device attempts to dereference NULL pointer
- Software crashes, causing monitoring system unavailability
- Manual restart/reboot required to restore functionality
Impact Assessment
- Central monitoring service crash
- Temporary system unavailability
- Requires manual intervention to restore
- Loss of real-time patient data visualization
- Interruption of alarm systems
- Potential monitoring gaps during downtime
- Manual restart procedures required
- Operational workflow disruption
- Need for backup monitoring protocols
Mitigation Strategies
Network Controls
- Network Segmentation: Isolate CNS-6201 on secure medical network
- Access Control: Restrict UDP communication to trusted devices only
- Firewall Rules: Block malformed or unexpected UDP packets
Security Measures
- Intrusion Detection: Deploy IDS to monitor for attack patterns
- Traffic Filtering: Implement deep packet inspection for UDP traffic
- Network Monitoring: Real-time monitoring of medical device communications
System Management
- Upgrade Path: Migrate to supported models (CNS-9601, CNS-9101)
- Incident Response: Implement automated restart procedures
- Alarm Escalation: Verify backup alarm systems during downtime
Resources and References
Official Documentation
End-of-Support Notice
The affected CNS-6201 versions are end-of-support (EoS). Organizations should prioritize migration to supported models to ensure continued security updates and vendor support.