ASKI Energy ALS-Mini-S8 and ALS-Mini-S4 Vulnerability
CVE-2025-62579 Code execution configuration compromise
Overview
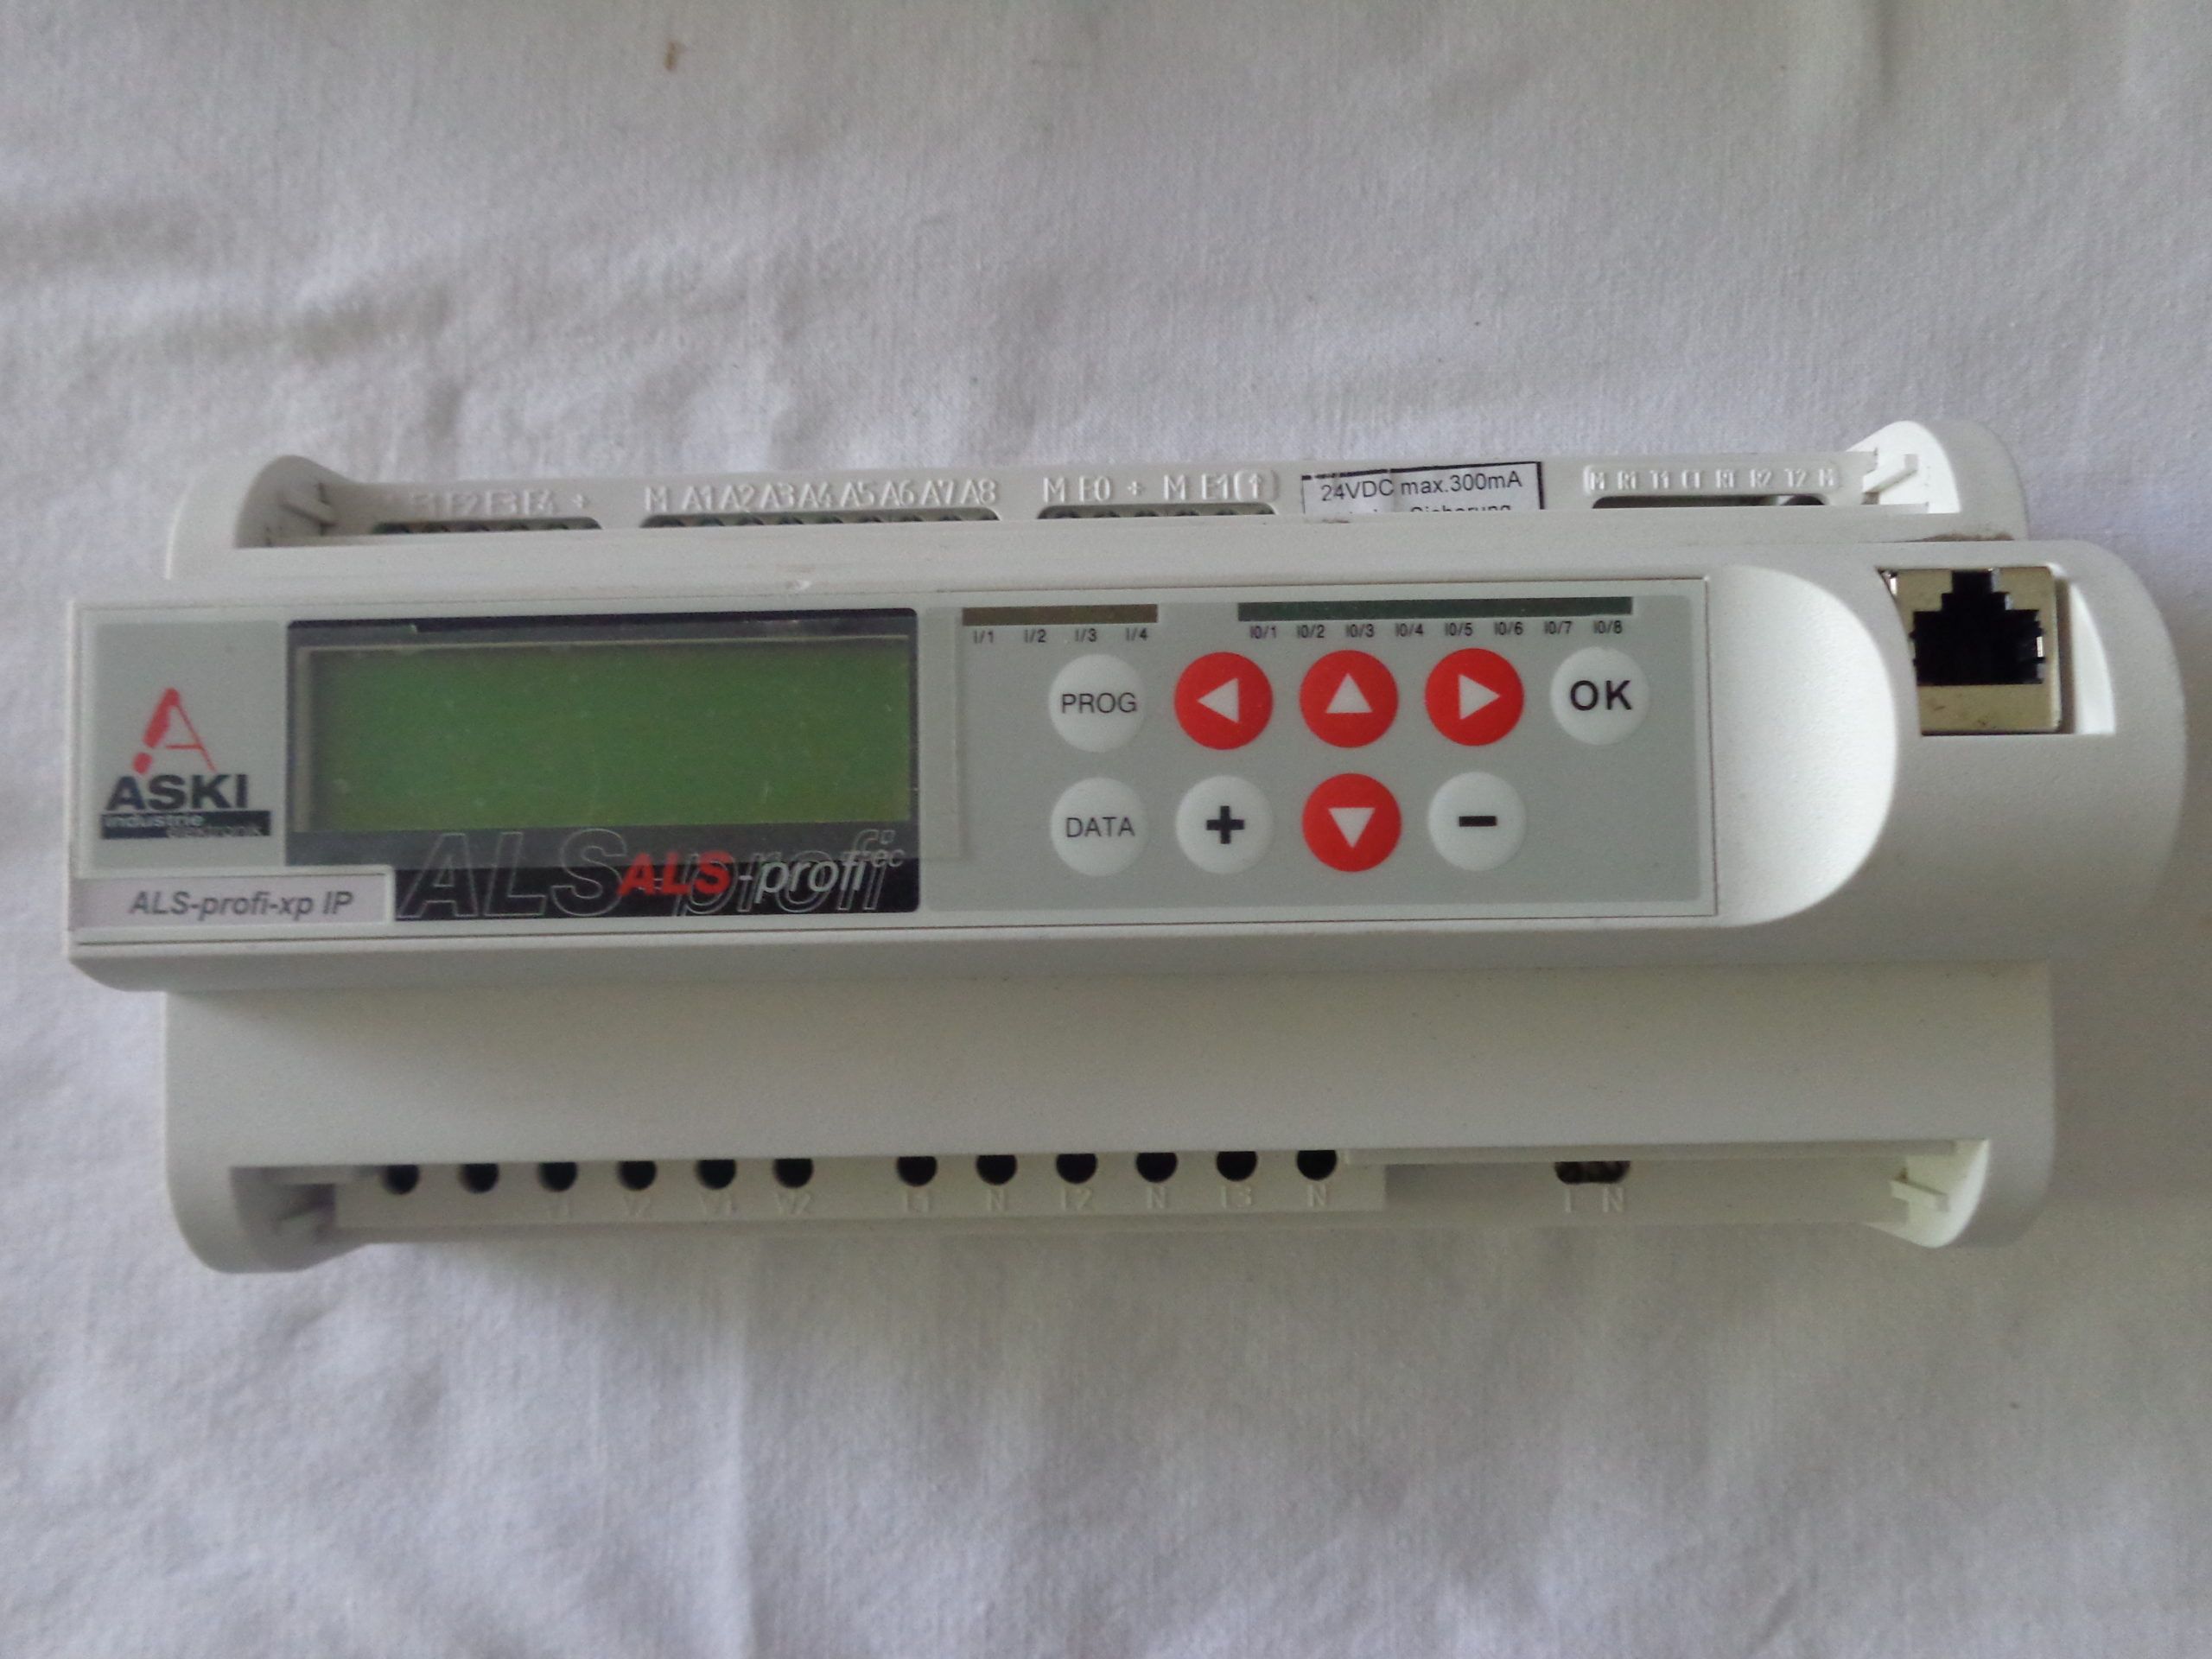
A critical security vulnerability in the embedded web server of ASKI Energy ALS-Mini-S4 and ALS-Mini-S8 IP controllers allows remote attackers to access and modify configuration parameters without authentication. The flaw provides full administrative control over affected devices, compromising their operational integrity.
Technical Specifications
| Attribute | Details |
|---|---|
| CVE ID | CVE-2025-9574 |
| Vulnerability Type | Missing Authentication for Critical Function (CWE-306) |
| Attack Vector | Network (remote over IP) |
| Authentication | None required |
| Complexity | Low |
| User Interaction | Not required |
Affected Products
- ALS-Mini-S4 IP and ALS-Mini-S8 IP controllers
- Serial Numbers: 2000–5166
- Firmware Versions: All versions affected
- Status: End-of-Life (EoL) since 2022
Attack Scenario
- Attacker connects to the same network as the ALS-Mini device
- Accesses the embedded web interface without credentials
- Sends HTTP requests to configuration endpoints
- Reads or modifies device settings remotely
- Takes full administrative control of the controller
Potential Access Points
- Direct network access to device IP
- Internet exposure if web server is publicly accessible
- SCADA/industrial network infiltration
Impact Assessment
- Full compromise of device configuration
- Unauthorized modification of load control logic
- Alteration of thresholds and communication parameters
- Potential disabling of critical alarms
- Access to sensitive operational data
- Exposure of energy management parameters
- Visibility into industrial control settings
- Network topology reconnaissance
- Operational disruption through misconfiguration
- Load imbalance and system downtime
- Energy management failures
- Service interruption potential
- Entry point for deeper SCADA network attacks
- Lateral movement opportunities
- Industrial network compromise risk
- Critical infrastructure exposure
Mitigation Strategies
Network Isolation
- Internet Exposure: Never expose affected devices to the Internet
- Firewall Protection: Place devices behind firewalls with strict rules
- IP Whitelisting: Limit network access to trusted, whitelisted IPs only
- Network Segmentation: Isolate from critical SCADA networks
Access Controls
- Secure Proxy: Use authenticated proxy for remote configuration needs
- VPN Access: Require VPN for any remote management
- Physical Security: Disconnect Ethernet if web server unused
- Local Operation: Device functions locally without network connectivity
Monitoring & Detection
- IDS/IPS Deployment: Monitor network access patterns
- Unauthorized Access Alerts: Alert on suspicious connection attempts
- Traffic Analysis: Log and analyze HTTP requests to devices
- Anomaly Detection: Monitor for configuration changes
Long-term Solutions
- Migration Planning: Replace with newer, supported ABB/ASKI models
- Asset Inventory: Identify all affected devices in environment
- Lifecycle Management: Plan end-of-life device replacement
- Vendor Support: Engage with ABB for migration assistance
Technical Recommendations
Immediate Actions
- Asset Discovery: Locate all ALS-Mini-S4/S8 devices in network
- Network Assessment: Verify current exposure and access controls
- Emergency Isolation: Disconnect Internet-facing devices immediately
- Access Review: Audit who currently has network access to devices
Short-term Measures
- Firewall Rules: Implement strict ingress/egress filtering
- Monitoring Setup: Deploy network monitoring for device access
- Documentation: Document all devices and their network configurations
- Incident Response: Prepare procedures for potential compromise
Long-term Strategy
- Replacement Planning: Budget and plan for device upgrades
- Security Architecture: Design secure industrial network topology
- Vendor Engagement: Work with ABB on migration timeline
- Training: Educate staff on secure industrial device management
Resources and References
Official Documentation
Critical Warning
These devices are end-of-life (EoL) since 2022. No security patches will be released. Immediate network isolation and migration planning are essential.
Emergency Response
If you suspect a device has been compromised: 1. Immediately isolate the device from the network 2. Check device logs for unauthorized configuration changes 3. Review network logs for suspicious access patterns 4. Reset device configuration to known-good state 5. Implement additional monitoring before reconnecting