This Week's Security Incidents
-
DoppelCart - Large-Scale Fake Online Shop Fraud Network
E-Commerce Fraud Fake Shops Card Theft Phishing Checkout Domain Churn
A large fraud network of about 119,000 fake shopping domains reportedly impersonates trusted retailers to steal payment-card and personal data through cloned checkout flows.
-
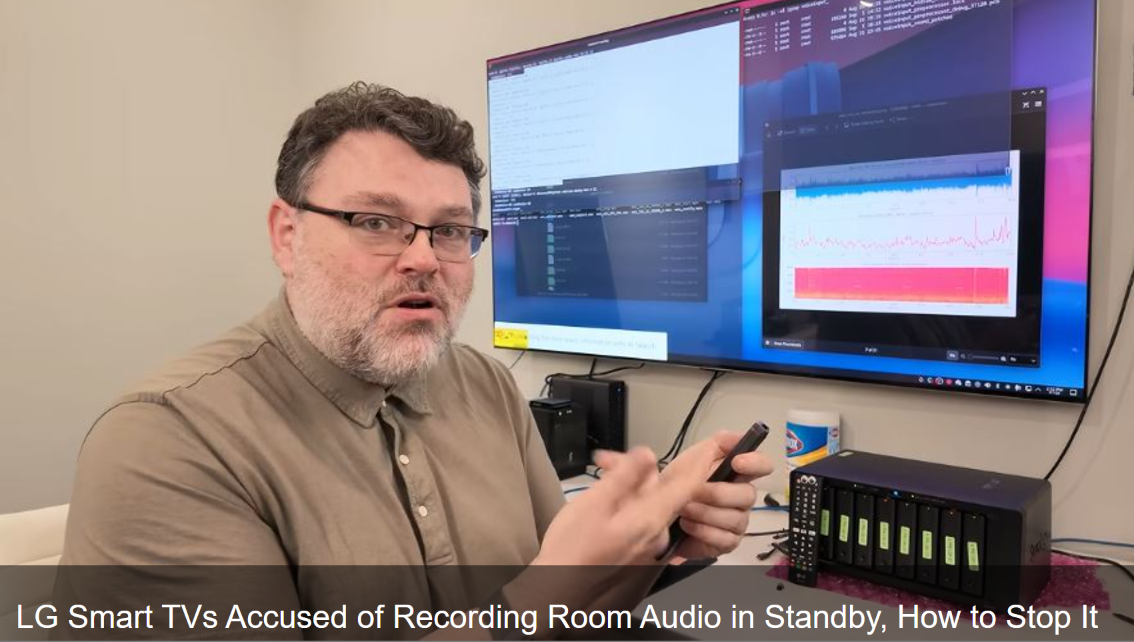
LG Smart TV Data Collection
Smart TV Privacy webOS ACR Telemetry IoT Exposure Standby Concerns
Researchers reported broad privacy concerns around ACR, telemetry, and standby behavior in LG webOS TVs, while LG disputes claims of secret recording and points to user controls.
-
WeWorm - WeChat Zero-Click Worm
WeChat Security Zero-Click Exploit Worm Propagation Cross-Platform Risk Account Takeover
Researchers demonstrated a zero-click WeChat call-handling exploit chain that can enable account takeover and worm-like spread across Android and iOS contact networks.
-
GitLab CVE-2026-85706 - Unauthenticated Path Traversal
CVE-2026-85706 Path Traversal Unauthenticated Access GitLab CE/EE KEV-Listed
A critical GitLab repository commits API flaw can allow unauthenticated arbitrary file read on vulnerable internet-facing instances, creating high risk of secret disclosure and follow-on compromise.