Handala Hack of Kash Patel (FBI Director) Personal Email
Account Compromise Hacktivism Data Leak
Overview
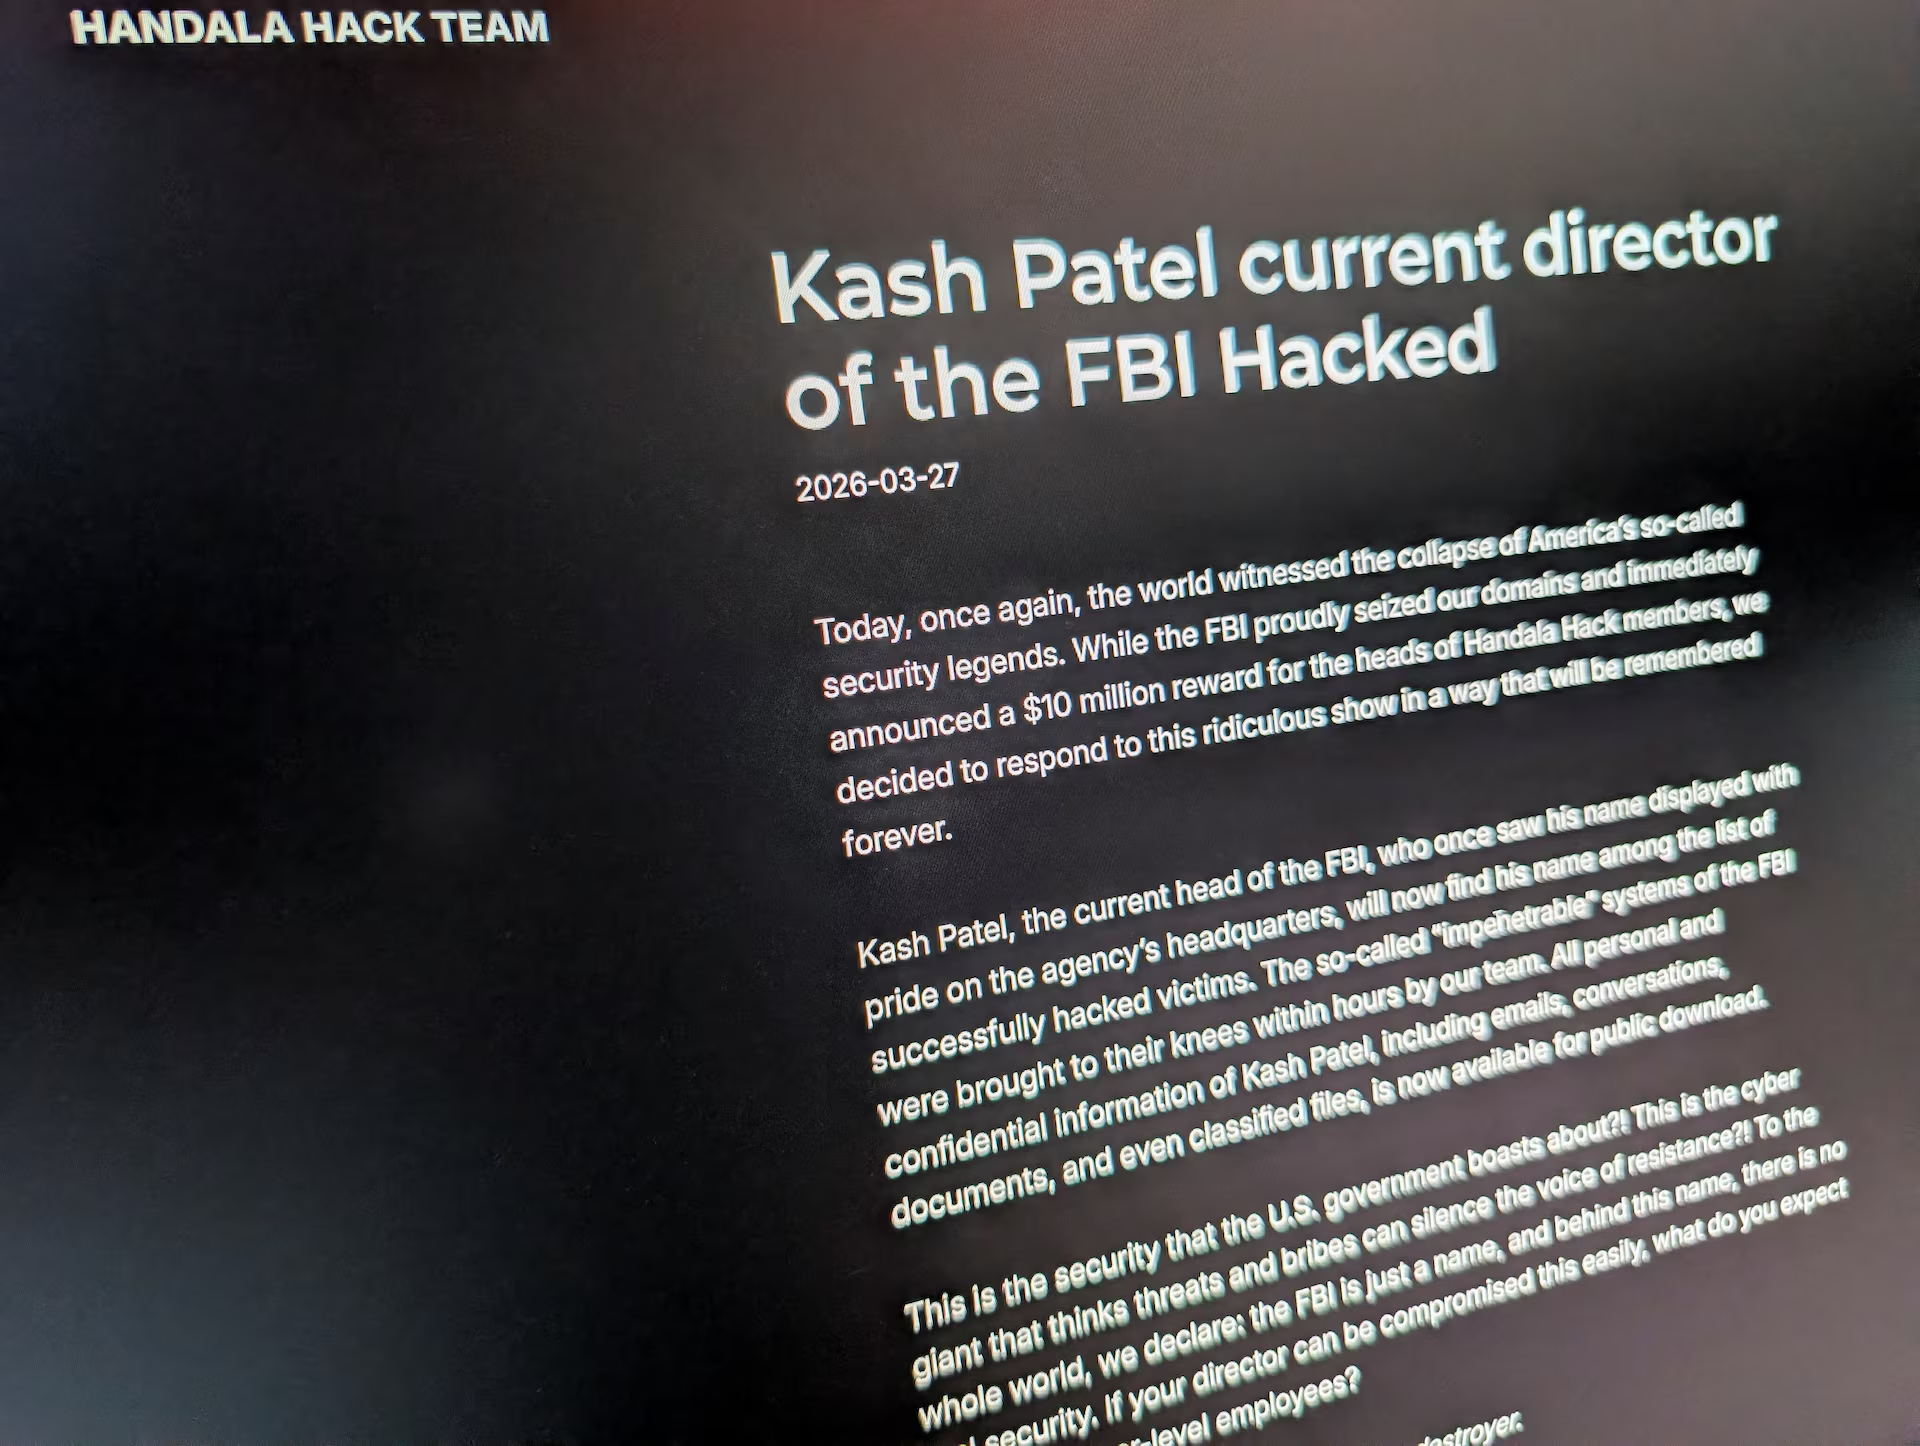
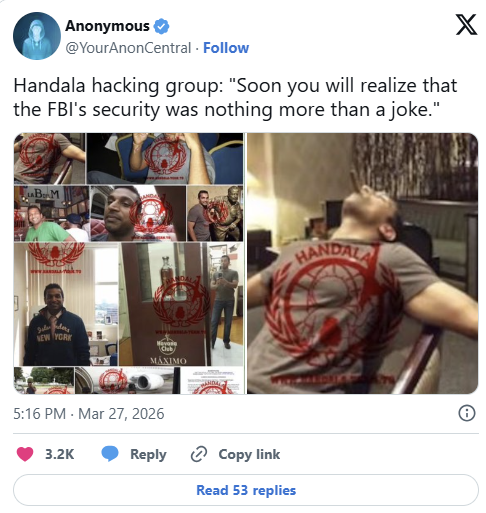
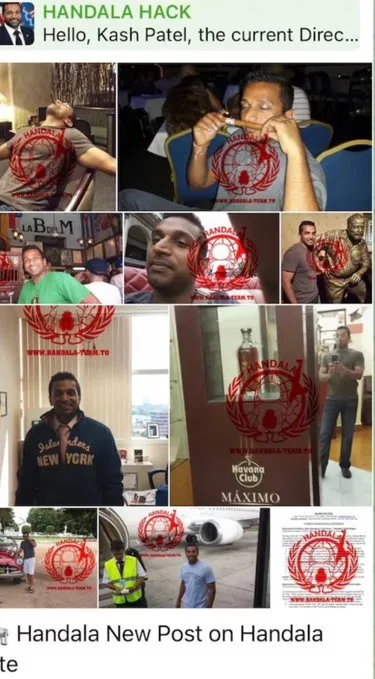
A pro-Iranian hacktivist group known as Handala claimed responsibility for compromising the personal email account of FBI Director Kash Patel and leaking hundreds of emails and personal files.
Public reporting indicates the exposed material was largely historical and personal in nature, with authorities stating that no classified information was compromised.
Technical Specifications
| Field | Details |
|---|---|
| Target | Personal email account (reportedly Gmail) |
| Threat Actor Claim | Handala (pro-Iranian hacktivist group) |
| Leaked Content | 300+ emails, personal photos, documents (resume/travel data) |
| Data Timeframe | Primarily 2010-2019 |
| Verification Notes | Reporting cites header analysis and signature validation |
| Classified Data Exposure | Not reported |
Affected Products
- Personal email account infrastructure associated with the target.
- Personal document/photo storage and communications content.
- Public information environment impacted by leak publication and amplification.
Technical Details
- Attackers claimed unauthorized access to a high-profile personal mailbox.
- Leaked datasets reportedly included emails, images, and personal documents.
- Public analyses referenced validation signals such as email-header consistency and cryptographic authenticity indicators.
- No confirmed evidence suggests compromise of official classified systems.
- Plausible access vectors include phishing, credential reuse, or social-engineering-assisted credential theft.
Attack Scenario
- Threat actors select a high-profile public official as the target.
- Credential access is obtained via phishing, reused credentials, or social engineering.
- Attackers access the personal email account and enumerate stored data.
- Content is exfiltrated and curated for publication.
- Leaks are released publicly to maximize reputational and psychological impact.
Impact Assessment
Personal and sensitive non-classified information was exposed, creating privacy and personal-security risks.
Public leak activity targeted a senior U.S. official, increasing reputational pressure and media amplification effects.
The case highlights persistent risk from personal-account compromise for high-profile individuals, even when official systems are not breached.
Mitigation Strategies
- Enforce multi-factor authentication (MFA) on personal and official accounts.
- Use strong, unique passwords and eliminate credential reuse.
- Maintain strict separation between personal and official communications.
- Adopt phishing-resistant authentication mechanisms (for example, hardware security keys).
- Monitor accounts continuously for suspicious login patterns and geolocation anomalies.
- Provide targeted security-awareness training for high-profile personnel and support staff.
Resources
Open-Source Reporting
- Iran-linked hackers breach FBI director's personal email, publish photos and documents | Reuters
- Iran-Linked Hackers Breach FBI Director's Personal Email, Hit Stryker With Wiper Attack
- Iran-linked group Handala hacked FBI Director Kash Patel's personal email account
- FBI director's personal email, photos and documents leaked by Iran-linked hackers | The Guardian
- Iranian hackers claim breach of FBI director Kash Patel's personal email account | TechCrunch
Last Updated: March 30, 2026