Siemens Energy Services Security Advisory
CVE-2025-59392 Authentication Bypass Physical Access Required
Overview
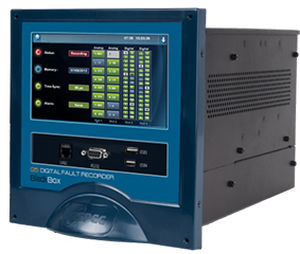
A security vulnerability has been identified in Siemens Energy Services products involving an authentication bypass using an alternate path or channel. The flaw affects Elspec G5 devices integrated with Siemens Energy Services and allows an attacker with physical access to circumvent authentication controls by inserting a USB drive containing a publicly documented reset string, enabling them to reset the administrative password and gain full control of the device.
Technical Specifications
| Attribute | Details |
|---|---|
| CVE ID | CVE-2025-59392 |
| Vulnerability Type | Authentication Bypass Using an Alternate Path or Channel (CWE-288) |
| Attack Vector | Physical |
| Authentication | Physical access required |
| Complexity | Low |
| User Interaction | Not required (once physical access obtained) |
| Affected Component | Elspec G5 devices integrated with Siemens Energy Services |
Affected Products
- Elspec G5 devices (through firmware version 1.2.2.19)
- Integrated with Siemens Energy Services
- Status: Patches available for versions beyond 1.2.2.19
Attack Scenario
- Adversary gains physical access to the environment where the impacted Elspec G5 device is installed
- Attacker inserts a USB storage device containing a specific reset string into the device's USB port
- The device improperly handles the alternate channel, allowing the attacker to bypass authentication and reset the administrator password
- Once admin credentials are reset, the attacker reconfigures or manipulates the system
- With administrative control, attacker could alter settings, disrupt operations, or compromise energy services workflows
Potential Access Points
- Physical access to facility housing Elspec G5 devices
- Insider threats with legitimate physical access
- Social engineering to gain entry to restricted areas
- Compromised physical security controls
Impact Assessment
- Full administrative control over device configuration
- Unauthorized modification of system settings
- Alteration of energy management parameters
- Potential disruption of critical infrastructure operations
- Access to sensitive operational data
- Exposure of energy services workflows
- Visibility into system configurations
- Potential credential harvesting
- Operational disruption of energy services
- System reconfiguration leading to downtime
- Critical infrastructure service interruption
- Potential cascading failures in energy systems
- Although exploit requires physical access, impact on critical infrastructure can be significant
- Unauthorized control of energy management systems
- Compliance and regulatory violations
- Reputational damage to critical infrastructure providers
Mitigation Strategies
🔄 Immediate Actions
- Apply Siemens firmware updates for Elspec G5 devices (upgrade beyond version 1.2.2.19)
- Review and restrict physical access to all Elspec G5 devices
- Conduct immediate physical security audit of device locations
- Disable or block USB ports if firmware update cannot be immediately applied
🛡️ Physical Security
- Access Restriction: Limit physical access to ICS gear to prevent unauthorized USB insertion or tampering
- Tamper Detection: Deploy tamper-evident seals and sensors on device enclosures
- Access Logs: Implement and monitor physical access logs for all critical device locations
- Security Personnel: Increase security presence in areas with vulnerable devices
🔍 Monitoring & Detection
- Monitor physical access logs and inspect USB port activity
- Deploy video surveillance in areas housing Elspec G5 devices
- Implement alerting for unauthorized physical access attempts
- Regularly audit administrative account activity and password changes
- Monitor for unexpected system reconfigurations
🔒 Access Management
- Use strong credential policies for all administrative accounts
- Limit shared administrative accounts
- Regularly review and rotate local admin credentials
- Implement multi-factor authentication where possible
- Maintain strict separation of duties for critical systems
📊 Network Segmentation
- Segregate ICS devices from general-purpose networks
- Implement defense-in-depth to limit lateral movement
- Apply zero-trust principles to industrial control systems
- Monitor and restrict network communications to/from Elspec G5 devices
Resources and References
Official Documentation
Critical Warning
This vulnerability requires physical access but affects critical infrastructure. Immediate firmware updates and physical security enhancements are essential to prevent unauthorized administrative access.