Hikvision & Rockwell Automation Critical Vulnerabilities Added to KEV Catalog
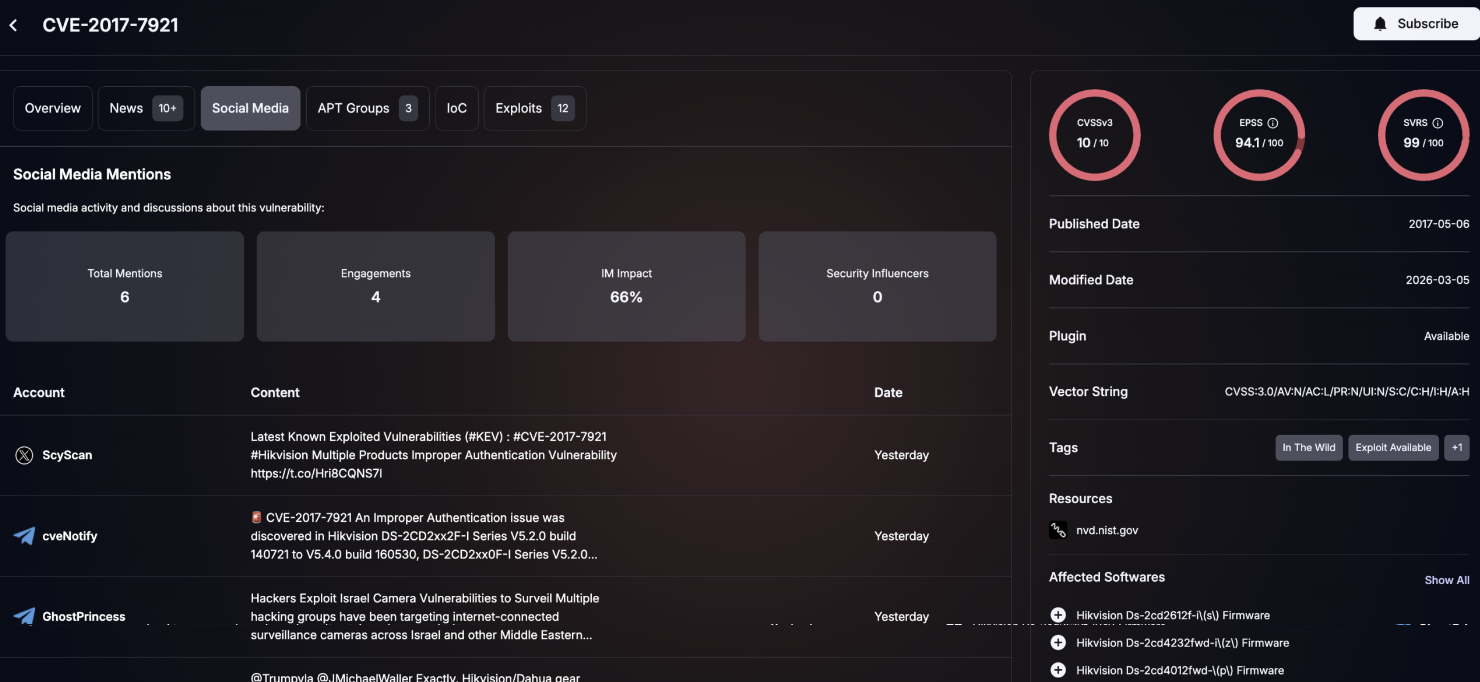
CVE-2017-7921 CVE-2021-22681 CISA KEV Critical Infrastructure Risk
Overview
CISA added two high-severity vulnerabilities affecting Hikvision surveillance systems and Rockwell Automation industrial software to the Known Exploited Vulnerabilities (KEV) Catalog. KEV inclusion indicates credible exploitation risk and urgent remediation priority for exposed organizations.
The issues impact both physical-security surveillance environments and industrial control workflows, raising risk of unauthorized monitoring, credential abuse, and potential operational disruption.
Technical Specifications
| Attribute | Details |
|---|---|
| CVE 1 | CVE-2017-7921 |
| Product Scope 1 | Hikvision IP cameras and surveillance systems |
| Issue Type 1 | Authentication bypass (improper auth controls) |
| CVSS 1 | 9.8 (Critical) |
| CVE 2 | CVE-2021-22681 |
| Product Scope 2 | Rockwell Automation ICS software (including Studio 5000 Logix Designer contexts) |
| Issue Type 2 | Credential exposure / weak credential protection |
| CVSS 2 | 9.8 (Critical) |
Affected Products
- Multiple Hikvision surveillance devices and management deployments impacted by CVE-2017-7921
- Rockwell Automation industrial environments using affected software workflows related to controller management
- Industrial/OT networks where engineering workstation trust can be abused
- Organizations with internet-exposed surveillance or weakly segmented ICS management paths
- Status: CISA KEV-listed; accelerated patching and hardening required
Technical Details
CVE-2017-7921 (Hikvision Authentication Bypass)
- Improper authentication logic allows bypass of normal login controls.
- Attackers can obtain elevated/administrator-level access on vulnerable camera systems.
- Unauthorized access can expose video feeds and sensitive device/network configuration data.
CVE-2021-22681 (Rockwell Credential Exposure)
- Weak credential protection can expose or enable misuse of authentication material.
- Attackers may impersonate trusted engineering workstations.
- Compromise of trusted ICS management context can enable unsafe interaction with controllers.
KEV Significance
- KEV listing indicates active threat relevance and prioritized exploitation concern.
- Combined IT/OT and surveillance exposure increases organizational attack surface.
Attack Scenario
-
Target Discovery:
- Attacker scans for reachable Hikvision management interfaces or exposed industrial software paths.
-
Initial Compromise:
- Authentication bypass is used to access surveillance devices, or credential exposure is leveraged in industrial software contexts.
-
Privilege Abuse:
- Attacker escalates operational control over camera systems or impersonates trusted engineering workstations.
-
Operational Manipulation:
- Surveillance: access to live feeds and configuration extraction.
- Industrial: potential controller logic/configuration manipulation via trusted channels.
-
Persistence and Expansion:
- Adversary establishes footholds for long-term reconnaissance, sabotage staging, or broader network pivoting.
Impact Assessment
- Unauthorized access to camera feeds and monitoring infrastructure
- Exposure of network topology and security configuration data
- Potential espionage and privacy violations through compromised surveillance systems
- Potential impersonation of trusted engineering workstations
- Elevated risk of unsafe PLC logic/configuration changes
- Operational disruption across manufacturing, utilities, and critical infrastructure sectors
- Increased likelihood of targeted exploitation due to KEV visibility
- Higher incident response burden across converged IT/OT environments
- Risk of sabotage, service downtime, and reputational damage
Mitigation Strategies
Patch and Firmware Management
- Apply latest Hikvision firmware updates addressing known auth bypass exposure
- Install Rockwell Automation security patches for affected software versions
- Prioritize KEV-listed remediation in vulnerability management workflows
Exposure Reduction
- Restrict management interfaces to trusted networks only
- Enforce strong network segmentation between IT, surveillance, and OT control layers
- Disable unnecessary externally reachable services
Authentication and Monitoring
- Enforce strong credential policies and access controls on admin/engineering accounts
- Monitor for unusual access attempts, unauthorized config changes, and anomalous engineering actions
- Integrate KEV advisories into threat-hunting and detection use cases
Resources and References
Open-Source Reporting
- Hikvision and Rockwell Automation CVSS 9.8 Flaws Added to CISA KEV Catalog
- CISA Adds Hikvision and Rockwell Automation CVSS 9.8 Flaws to KEV Catalog
- U.S. CISA adds Apple, Rockwell, and Hikvision flaws to its Known Exploited Vulnerabilities catalog
- CISA Flags Hikvision Camera & Rockwell Logix Vulnerabilities as Actively Exploited
Last Updated: March 8, 2026