Brinks Home The most famous brand in physical security got pwned by ShinyHunters
Data Extortion ShinyHunters Unauthorized Access Potential Data Exfiltration Smart Home Sector
Overview
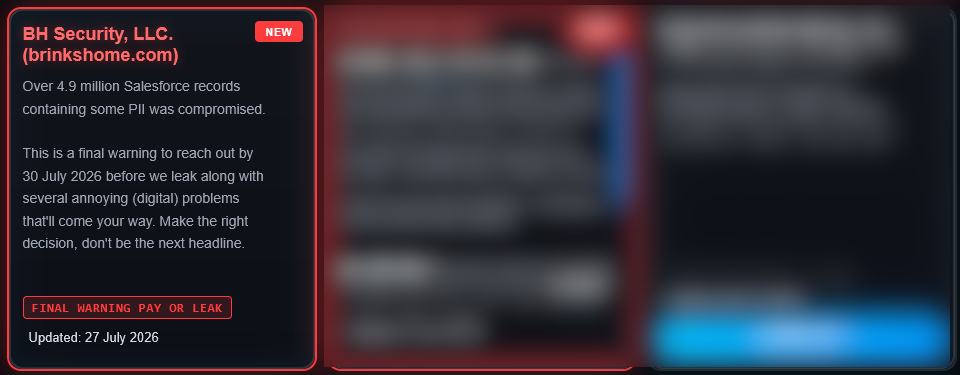
The cybercriminal group ShinyHunters claimed responsibility for breaching Brinks Home, a U.S.-based smart home security provider. The threat actor alleged theft of sensitive company data and threatened publication on its leak site unless ransom demands were met.
Brinks Home confirmed unauthorized access to portions of its network and initiated an investigation with external cybersecurity specialists. At reporting time, not all attacker claims had been independently verified.
Technical Specifications
| Attribute | Details |
|---|---|
| Threat Actor Claim | ShinyHunters data-extortion operation |
| Confirmed Condition | Unauthorized access to portions of Brinks Home internal network |
| Suspected Attacker Action | Data collection and exfiltration prior to discovery |
| Extortion Channel | Listing on leak site with threat of public data release |
| Encryption Activity | No public evidence of ransomware encryption reported |
| Service Impact | No confirmed broad service disruption reported at disclosure time |
| Investigation Status | Active, including scope validation and initial access determination |
| Known Unknowns | Full data scope, affected populations, and precise intrusion path remain under review |
Affected Products
- Brinks Home corporate network segments involved in the unauthorized access event
- Potentially exposed business and customer data stores under investigation
- Internal systems tied to identity, administration, and data handling workflows
Attack Scenario
- Attackers gained unauthorized access to Brinks Home corporate infrastructure (initial vector not publicly disclosed).
- The intruders escalated privileges and conducted internal discovery.
- Sensitive data was allegedly collected and exfiltrated.
- ShinyHunters posted extortion claims and threatened public leak-site publication unless ransom demands were met.
- Brinks Home initiated incident response, external forensics, and verification efforts.
Impact Assessment
- Unauthorized access and privilege escalation can undermine trust in internal administrative boundaries
- Potential tampering opportunities may exist pending full forensic scope confirmation
- Data-extortion pressure can influence operational and legal decision pathways
- Possible exposure of customer and corporate data if exfiltration is confirmed
- Stolen information may enable targeted phishing, fraud, or identity abuse
- Leak-site publication risk increases downstream exposure to secondary threat actors
- No major outage has been publicly confirmed, but response operations can impact business workflows
- Containment, remediation, and notification requirements may create prolonged operational overhead
- Future disclosures could trigger additional legal/compliance-driven disruption
Mitigation Strategies
Immediate Actions
- Enforce MFA for all users, prioritizing privileged and externally accessible accounts
- Isolate affected segments and validate suspicious account activity
- Initiate rapid credential reset and session revocation for high-risk identities
Short-term Measures
- Implement least-privilege access controls and remove unnecessary privileged pathways
- Segment sensitive systems and restrict east-west movement opportunities
- Encrypt sensitive data at rest and in transit where not already enforced
Monitoring & Detection
- Continuously monitor authentication anomalies and large-scale data transfer patterns
- Deploy or tune EDR/XDR telemetry for lateral movement and exfiltration behaviors
- Maintain alerting for leak-site references and extortion-related intelligence indicators
Long-term Solutions
- Conduct recurring security awareness and phishing-resilience training
- Maintain tested incident response and backup/recovery plans
- Perform regular security assessments, attack-surface reviews, and vulnerability audits
Resources and References
Public Reporting
Last Updated: August 2, 2026