Cisco Catalyst SD-WAN Manager Authentication Bypass
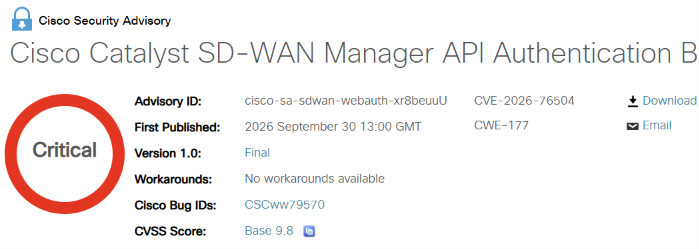
Cisco SD-WAN Manager CVE-2026-76504 Authentication Bypass Active Exploitation
Overview
Cisco disclosed a critical authentication-bypass vulnerability in the API session-authentication mechanism of Cisco Catalyst SD-WAN Manager.
The flaw allows an unauthenticated remote attacker to bypass authentication and obtain API access with administrator privileges. Cisco confirmed active exploitation in September 2026.
Technical Details
CVE-2026-76504 is caused by improper handling of URI encoding (CWE-177).
Attackers can manipulate encoded characters in HTTP requests to bypass the authentication rule protecting the j_security_check endpoint. Cisco identified request patterns such as /%6a_security_check, where %6a represents j.
- No valid credentials are required.
- No user interaction is required.
- Exploitation targets API session-authentication controls.
Technical Specifications
| Attribute | Details |
|---|---|
| CVE | CVE-2026-76504 |
| Component | Cisco Catalyst SD-WAN Manager API session-authentication mechanism |
| Weakness | Improper handling of URI encoding (CWE-177) |
| Exploit Characteristic | Encoded-path manipulation bypassing j_security_check protection |
| Privilege Obtained | Administrator-level API access |
| Exploitation Status | Cisco-confirmed active exploitation (September 2026) |
Affected Products
- Cisco Catalyst SD-WAN Manager deployments running vulnerable releases.
- Internet-exposed management interfaces are especially high risk.
Attack Scenario
- Attacker identifies an exposed Cisco Catalyst SD-WAN Manager instance.
- Attacker sends a specially crafted HTTP request containing URI-encoded characters.
- Authentication controls are bypassed.
- Attacker obtains administrative API access.
- Attacker can modify SD-WAN configurations or perform other privileged management operations.
Impact Assessment
- Unauthorized administrator-level access to SD-WAN Manager API
- Potential manipulation of SD-WAN policies and centralized network control
- Unauthorized configuration changes may disrupt connectivity and services
- Sensitive management information may be exposed
- Centralized compromise can impact multiple connected sites
- Critical due to unauthenticated remote exploitability and administrator-level access
Mitigation Strategies
- Upgrade to fixed Cisco releases as soon as possible.
-
Fixed releases include:
20.9.10.120.12.8.220.15.6.120.18.4.126.1.2.126.2.1
-
Restrict Internet exposure of SD-WAN Manager.
- Permit management access only from trusted networks.
- Apply firewall controls around management interfaces.
- Monitor authentication and API logs for anomalous requests.
- Investigate suspicious URI-encoded requests targeting authentication endpoints.
Cisco states there is no workaround that fixes the vulnerability itself.
Resources and References
Public Reporting
Last Updated: October 1, 2026