Festo Compact Vision System – Insecure Configuration Vulnerabilities
Exposure of Resources
Insecure Defaults
ICS/OT Systems
Overview
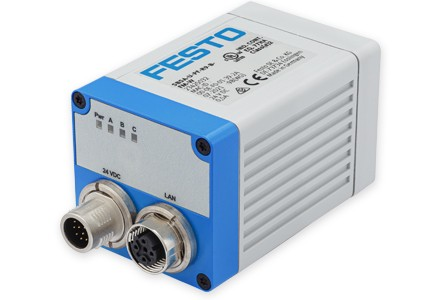
The advisory warns that certain Festo products — Compact Vision System, Control Block, Controller, and Operator Unit — contain one or more vulnerabilities that could be exploited by attackers. The nature of the vulnerability relates to insecure configuration or exposure of resources, potentially allowing unauthorized access to critical industrial control systems.
Technical Specifications
| Attribute | Details |
|---|---|
| Affected Products | Festo Compact Vision System, Control Block, Controller, Operator Unit |
| Vulnerability Type | Exposure of Resource to Wrong Sphere, Insecure Default Initialization |
| Attack Vector | Network (Remote) |
| Attack Complexity | Low |
| Authentication | None or minimal required |
| Affected Environment | ICS/OT Industrial Control Systems |
Vulnerability Details
The vulnerabilities are described generally as: - Exposure of resource to wrong sphere - Initialization of a resource with an insecure default
This suggests that internal resources (configuration interfaces, control endpoints, services) are exposed — possibly without authentication or proper access control — or initialized with insecure defaults, creating a weakness an attacker could exploit.
The "low / remote" attack complexity indicated by the advisory suggests that exploitation could be done remotely, without complicated prerequisites.
Attack Scenario
-
Network Access: An attacker obtains network access to the segment hosting the affected Festo devices (e.g., through lateral movement, compromised host, weak network segmentation, or exposed interface).
-
Exploitation: Due to insecure default configuration or exposed resources, the attacker connects to the device without needing valid credentials.
-
Unauthorized Access: The attacker interacts with configuration/control interfaces and gains unauthorized access or control over the device.
-
Impact on Operations: Because these are ICS/OT systems, this could lead to:
- Manipulation of control logic
- Configuration changes
- Disruption of operations
- Sabotage
Impact Assessment
- Unauthorized access to critical ICS equipment
- Modification of configuration or control logic
- Disruption or sabotage of automated/industrial processes
- Safety hazards or operational downtime
- Potential physical damage to equipment or processes
- Broader risk if ICS network is connected to enterprise networks
- Possible lateral movement or further compromise
- Gateway to other critical infrastructure
Mitigations
🔍 Inventory & Assessment
- Inventory your systems — check whether you deploy the affected Festo products (Compact Vision System, Control Block, Controller, Operator Unit)
🔄 Patching & Updates
- Immediately apply any patches or firmware updates released by Festo (or follow vendor guidance) if/when available
🌐 Network Segmentation
- Segregate ICS/OT networks from enterprise/IT networks
- Restrict access — ideally place ICS devices behind firewalls or isolated network zones
🔒 Access Control
- Restrict remote access: disable unnecessary remote interfaces
- Enforce authentication and least-privilege
- Review and harden configuration: avoid insecure default settings
- Disable unnecessary services
- Ensure secure initialization
📊 Monitoring & Logging
- Monitor and log access to ICS devices
- Scrutinize unexpected connections or configuration changes
🛡️ Defense-in-Depth
- Implement network segmentation
- Deploy intrusion detection on OT network
- Enforce strict access controls