Security Operations Briefing
Incidents
A living, day-by-day catalogue of cybersecurity incidents, vulnerabilities, malware campaigns, and threat-actor activity — each entry a standalone briefing on what happened, what's affected, and what to do about it.
Tuesday, November 10, 2026
-
Critical Android Zero-Click Remote Code Execution Vulnerability
Android CVE-2026-58868 Zero-Click Heap Overflow Framework
Google patched a critical Android framework flaw that may enable remote code execution on Android 14 to 17 without user interaction.
-
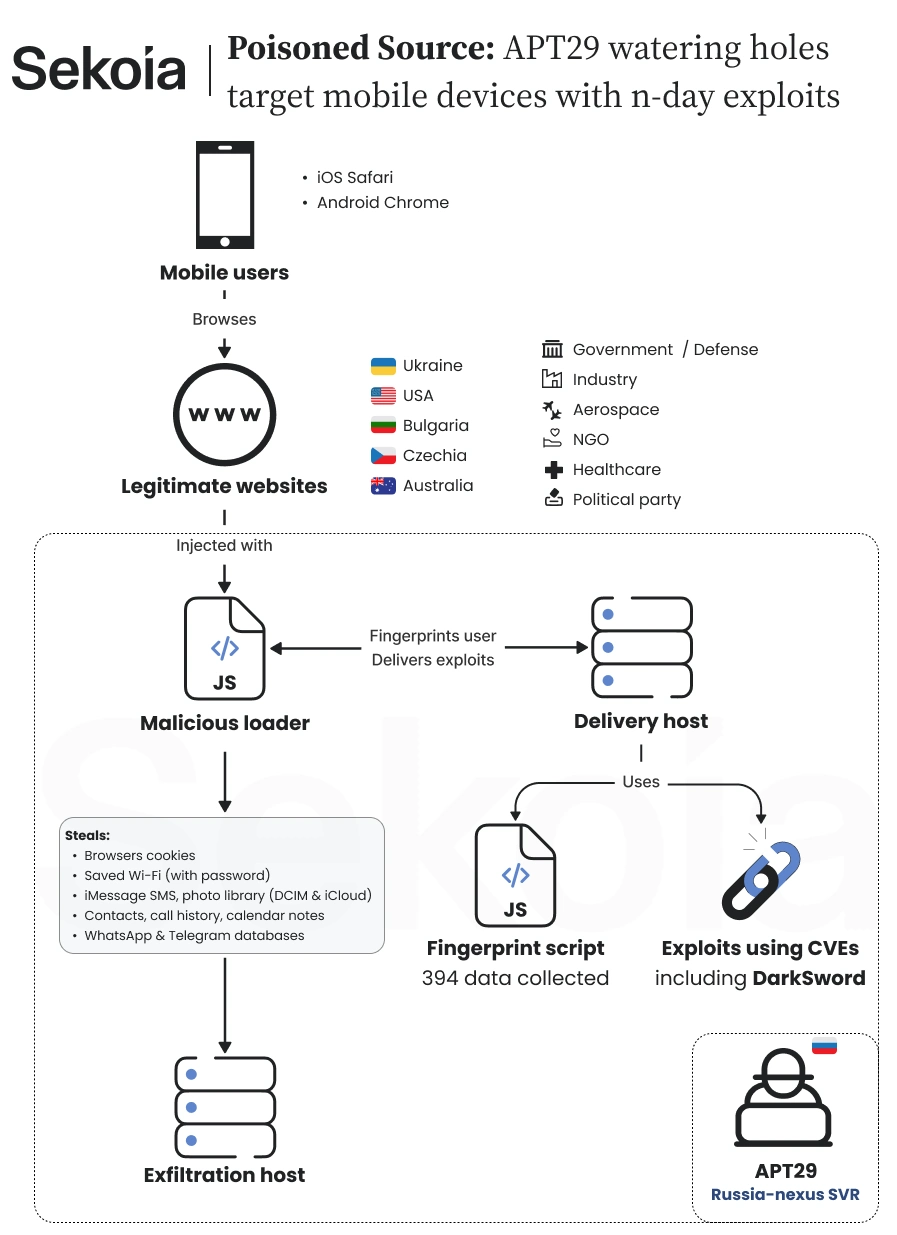
APT29 Mobile Watering Hole Campaign
APT29 iOS/Android Exploits Watering Hole Plerdy Supply-Chain Data Exfiltration
Sekoia-reported activity used compromised sites and analytics supply chain access to fingerprint mobile visitors and deliver targeted exploit chains.
-
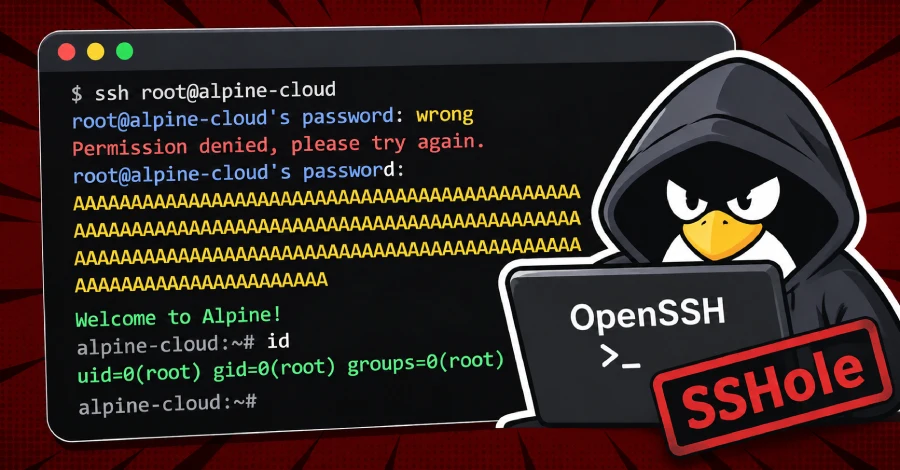
OpenSSH SSHole Authentication Bypass
OpenSSH CVE-2026-123158 SSHole Auth Bypass musl/PAM Condition
A conditional OpenSSH flaw in musl-based environments can mis-handle failed password hashing and allow unauthorized SSH login bypass under specific account states.
-
Multiple Zero-Day Vulnerabilities in D-Link DGS-3130 Series Managed Switches
D-Link DGS-3130 Zero-Day DDP Weaknesses Switch Security Patch Pending
D-Link disclosed multiple unpatched DGS-3130 weaknesses that can expose management data and enable unauthorized switch operations from reachable network segments.